
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Humanitarian & nonprofit
Coordinates community complaints and safeguarding concerns through accessible reporting channels.
12 workspace menus · 5 role profiles · Connected records
Designed for programme coordinators and the responsible business owners
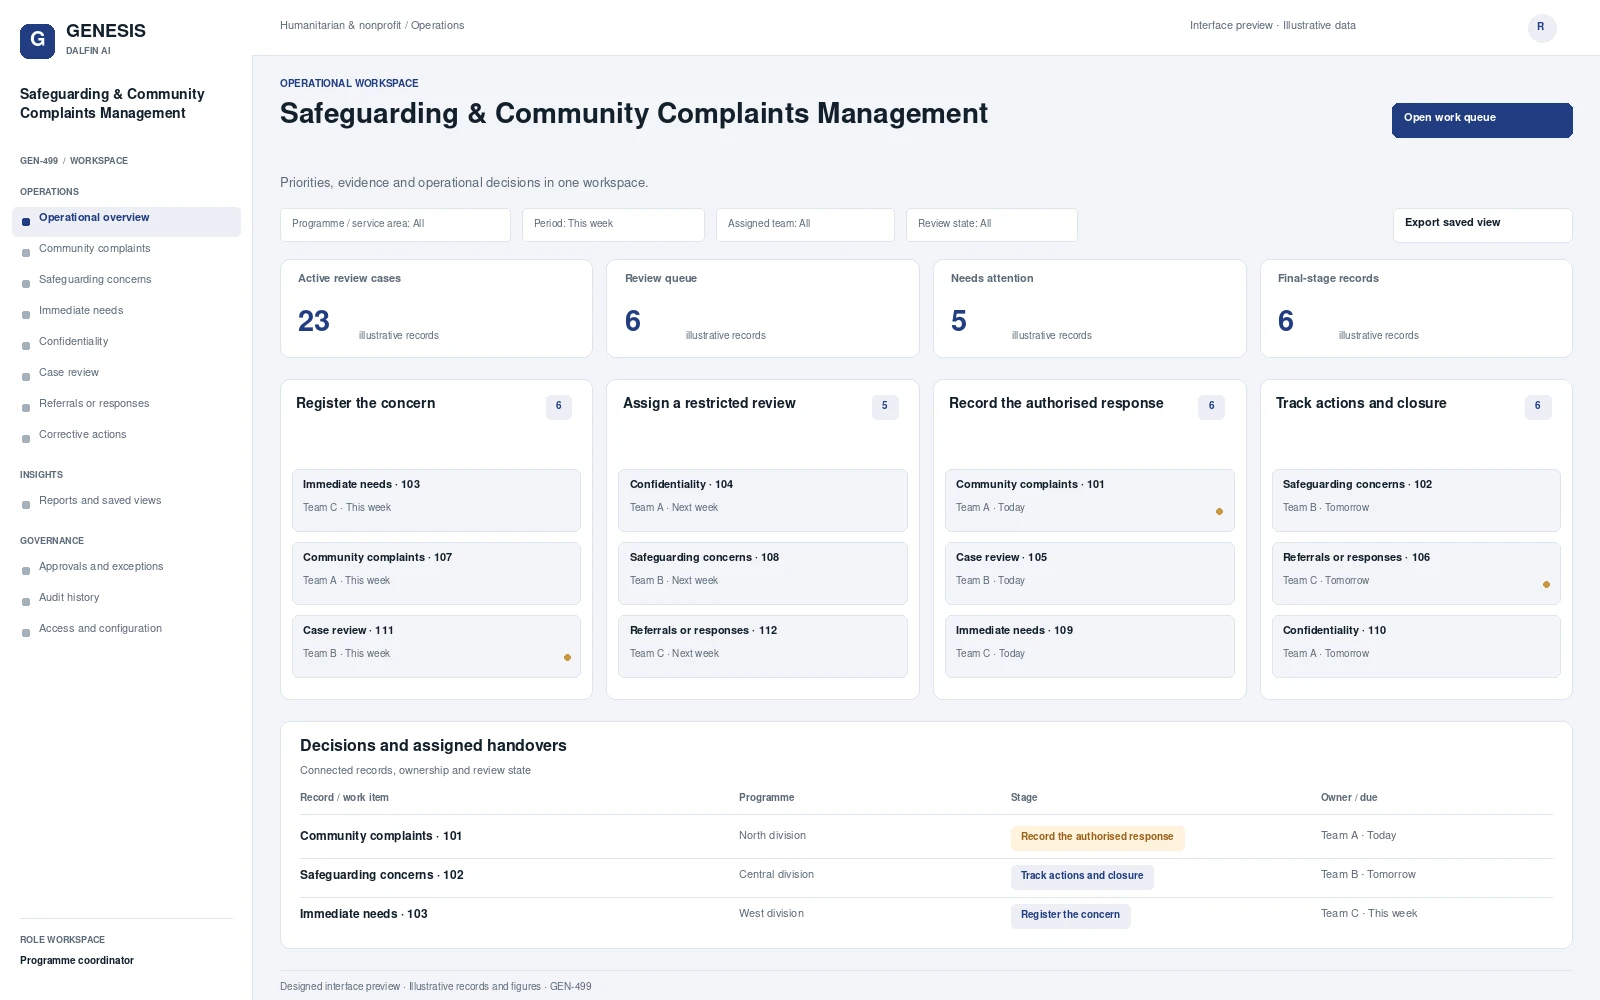
Operational workspace and record review. Select a screen to inspect it in full.
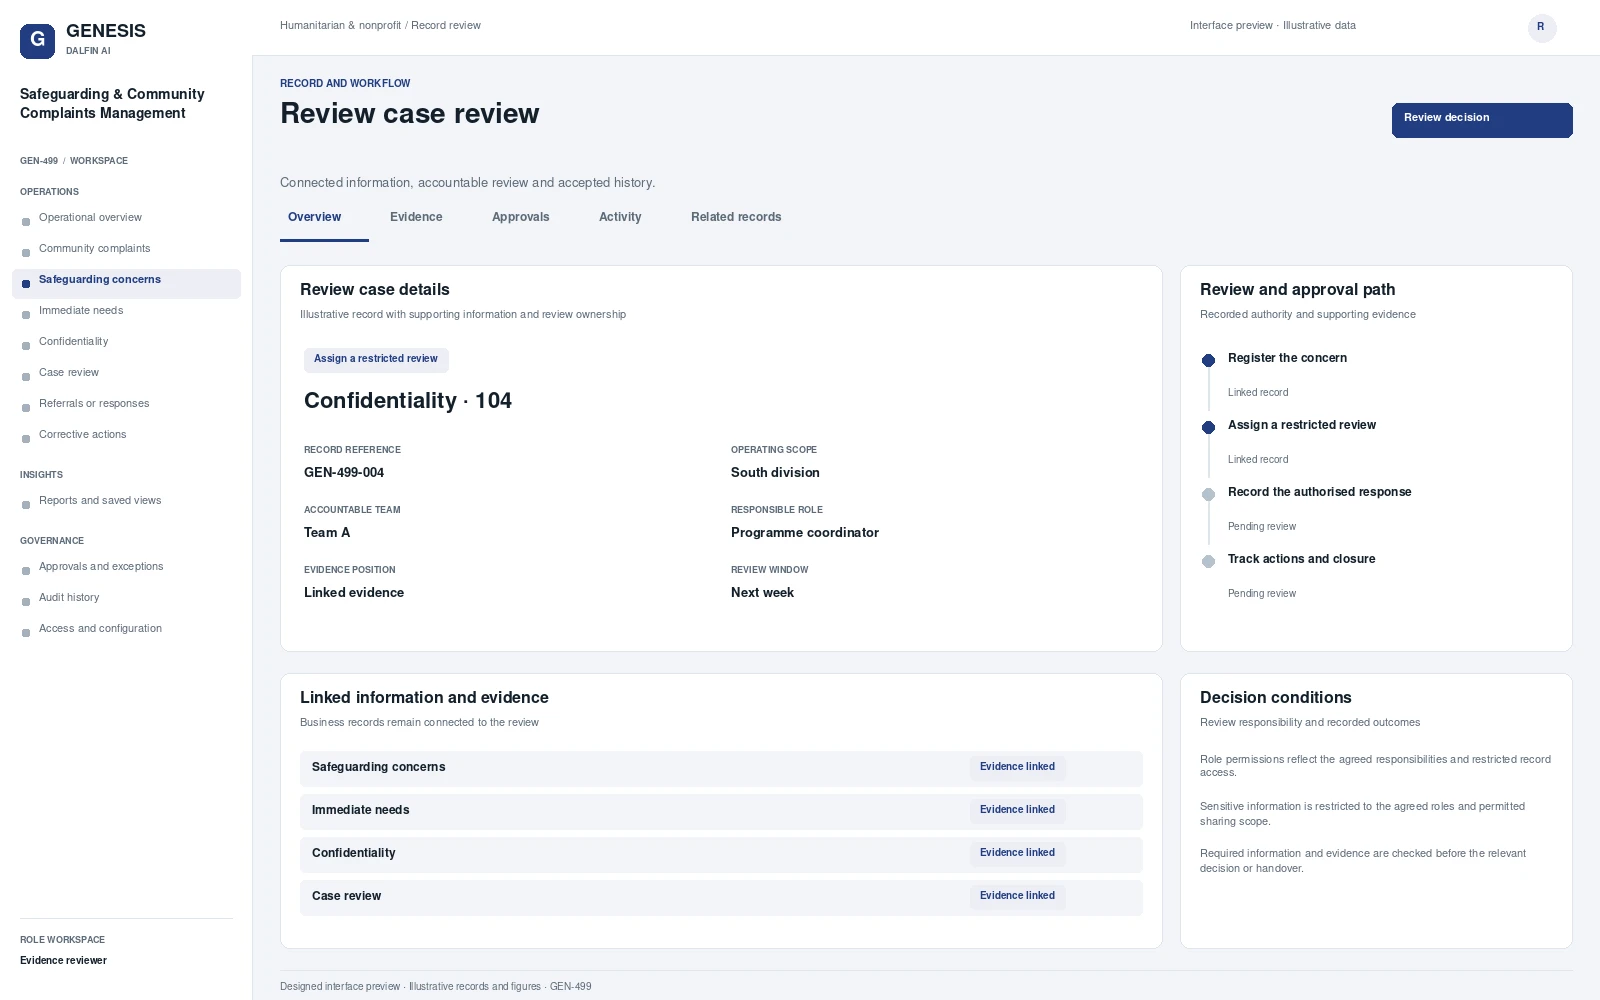
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Coordinates community complaints and safeguarding concerns through accessible reporting channels. Tracks immediate needs, confidentiality and authorised case review, records approved referrals or responses and monitors corrective actions with controlled communications and restricted supporting evidence.
From intake to authorised completion, with evidence at each decision.
Establish the scope of community complaints, capture the required records and assign the accountable team.
Coordinate safeguarding concerns and immediate needs with linked evidence and visible outstanding actions.
Review the relevant conditions and exceptions. Record the authorised outcome and its supporting evidence.
Confirm the resulting records and handovers. Track remaining obligations, later changes and follow-up actions.
Permissions are configured and tested for the agreed responsibilities.
Interface scope, data mapping and testing are agreed for each engagement.
Authorised users can review community complaints, supporting records and assigned actions through mobile and tablet access. The relevant tasks and permissions are agreed for the deployment.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Core workflows and approval rules are defined with your business owners. Operational AI can be assessed separately against a specific business outcome and review requirements.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
An example operating scenario
Start with community complaints and follow the record through the ‘Assign a restricted review’ stage. Introduce a missing item or operating exception, record the authorised resolution and inspect the final handover, evidence and history.
Review a representative review case, its workflow stages, accountable roles, an exception and the resulting operational report. Bring the business process and existing system requirements that matter to your organisation.
The operating scope covers your records, role permissions, review authority, business rules and integration boundaries. These requirements are agreed with the responsible business owners.
Connection design defines interfaces, data ownership, mapping, authentication and exception handling. The agreed implementation includes validation against the selected systems and workflows.
The agreed engineering approach covers review of change impact, bounded implementation, validation and accepted revisions. Discuss the relevant Genesis Context Memory and support requirements during solution scoping.
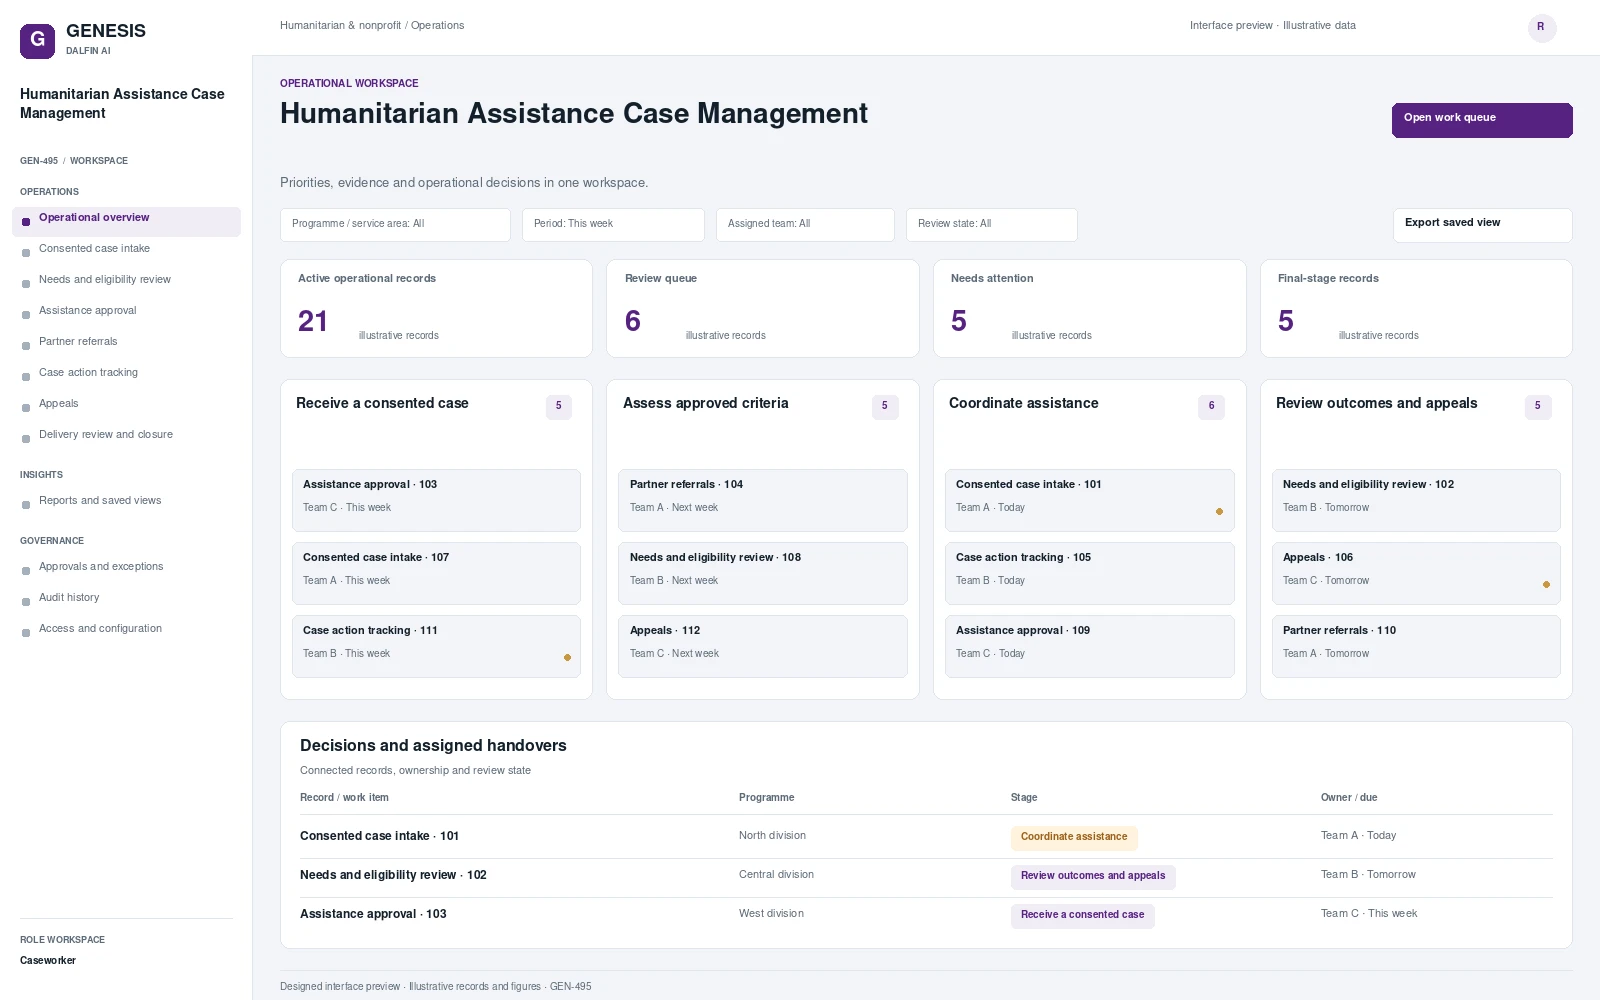 Interface preview
Coordinate consented case intake, approved eligibility review, assistance decisions, partner referrals, appeals and closure evidence.
Explore system →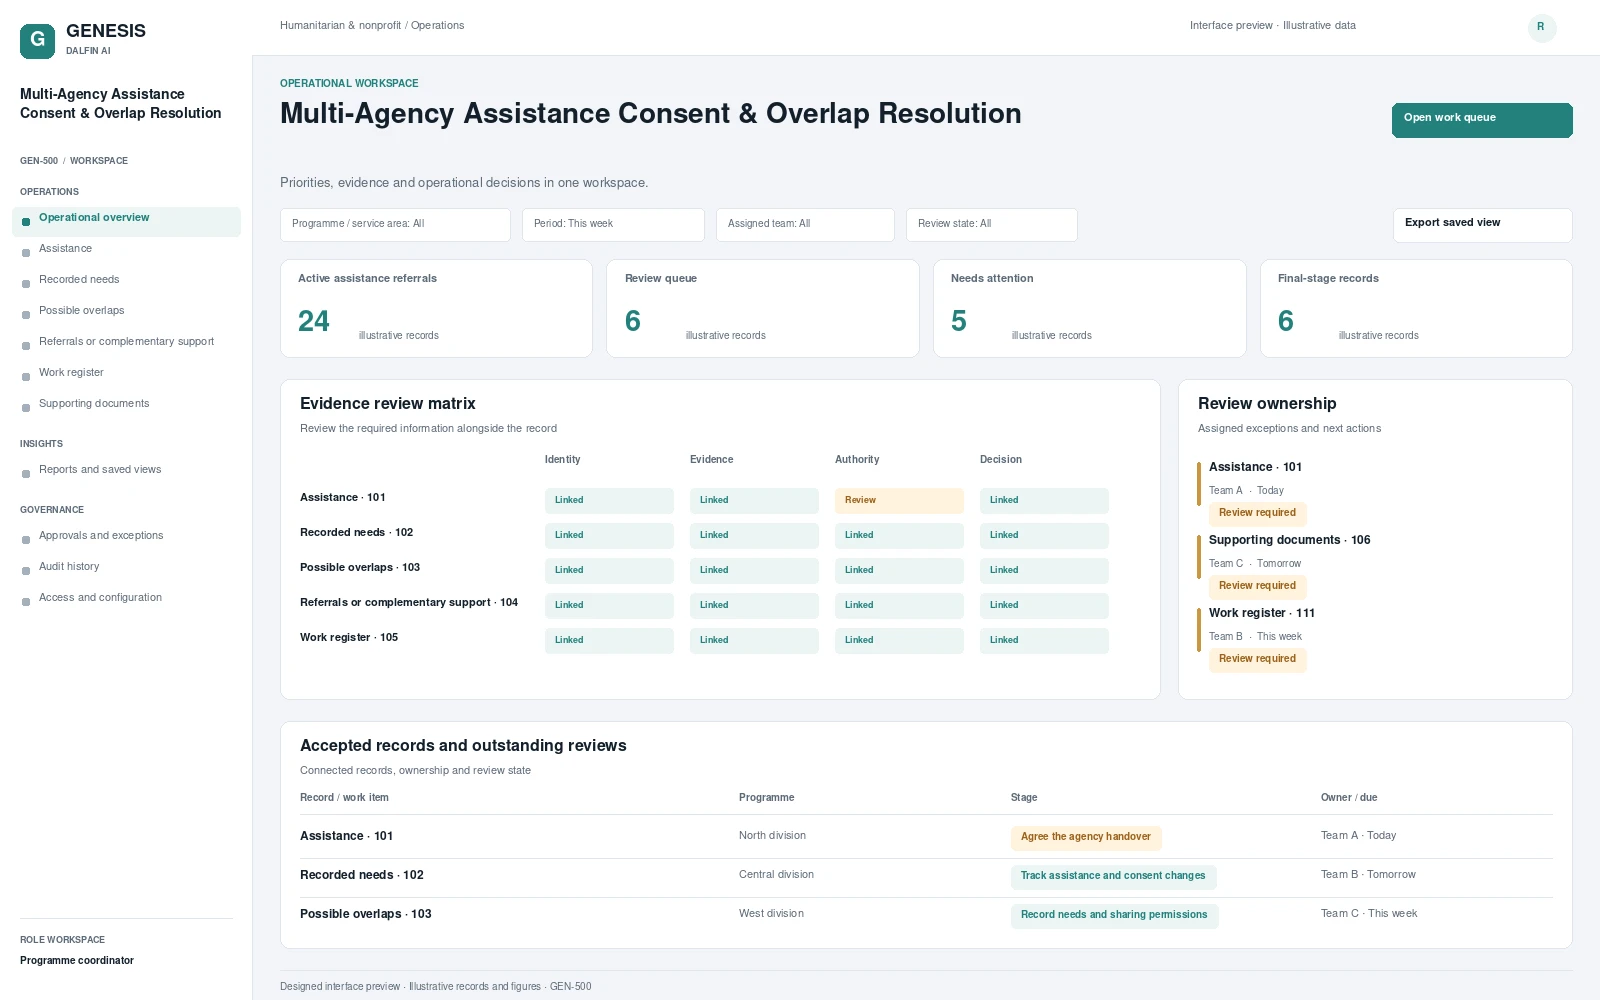 Interface preview
Coordinates assistance across agencies using appropriate sharing permissions and recorded needs.
Explore system → Interface preview
Manages volunteer opportunities, consented applications, required checks and induction.
Explore system →