
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Enterprise operations
Connect interpreted obligations to accountable control tasks, evidence submissions, exception review and approved reporting records.
12 workspace menus · 5 role profiles · Connected records
Designed for compliance directors and obligation owners
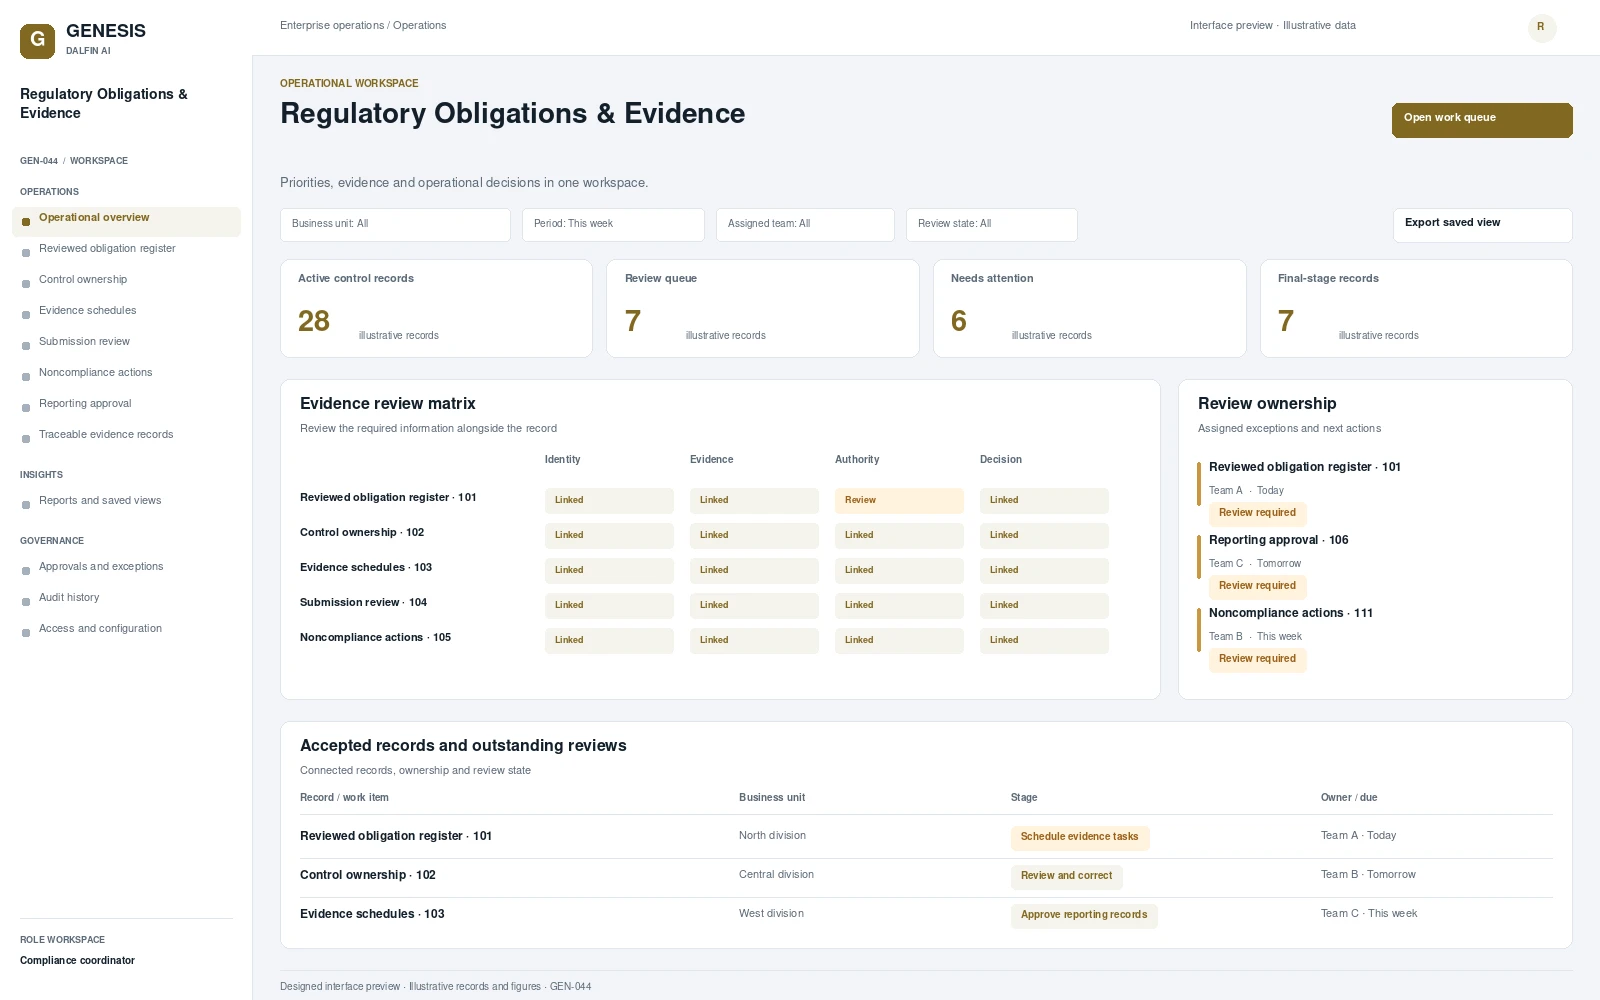
Operational workspace and record review. Select a screen to inspect it in full.
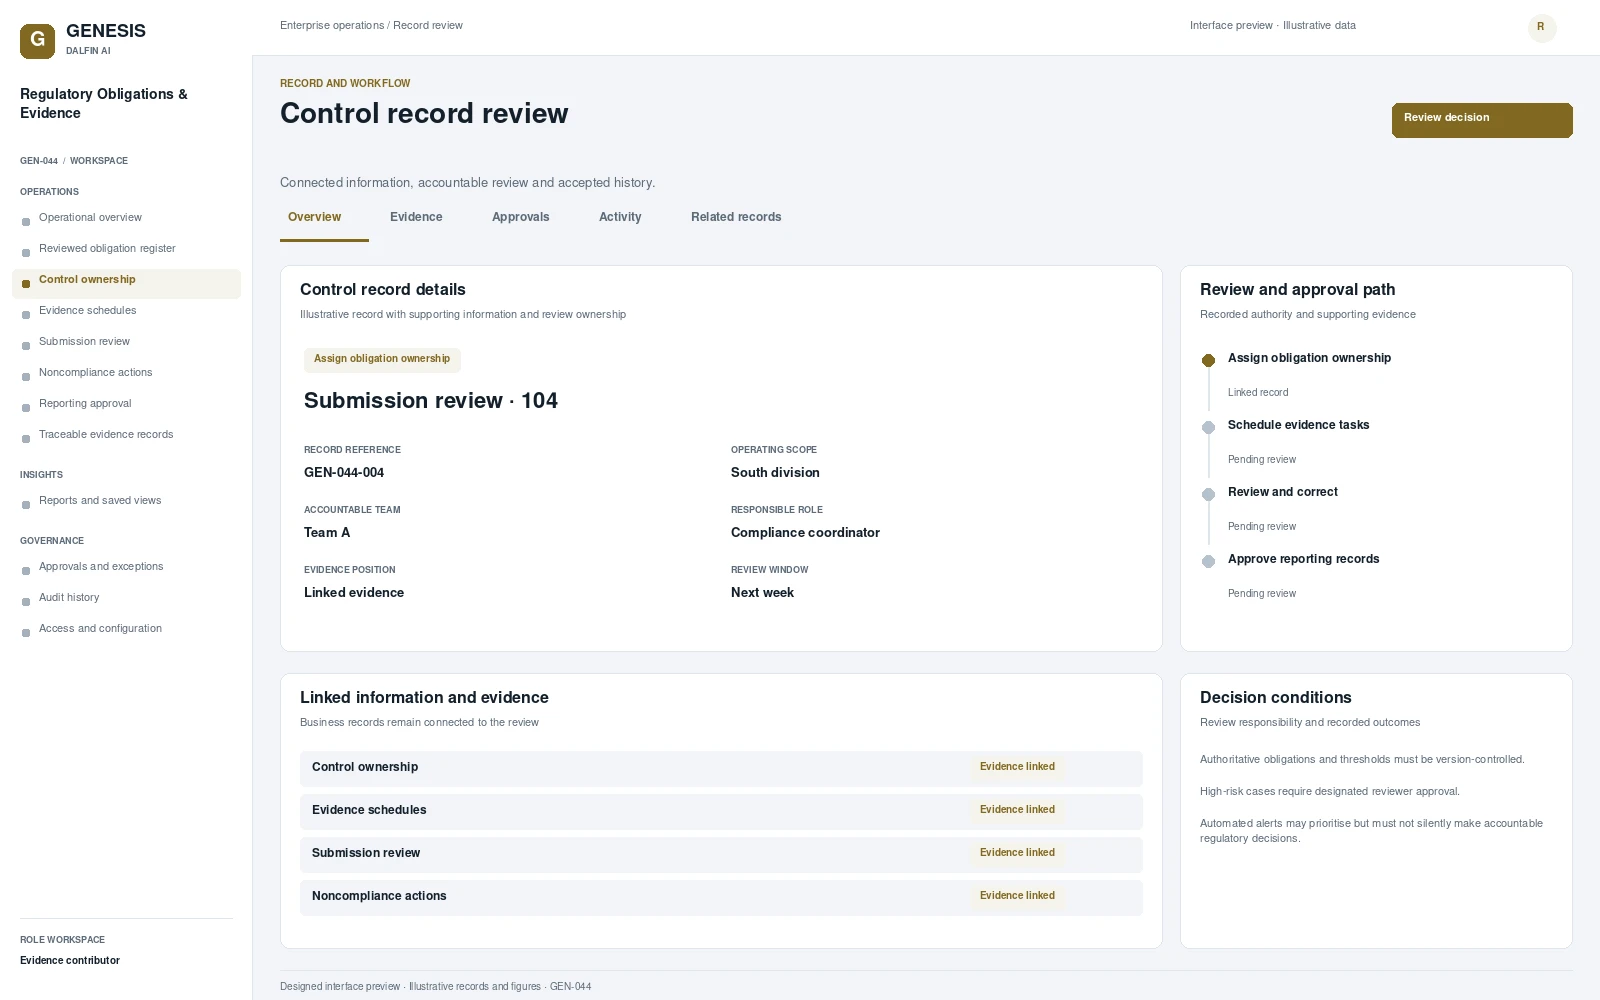
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Connect interpreted obligations to accountable control tasks, evidence submissions, exception review and approved reporting records. An obligation register becomes difficult to trust when requirements are detached from evidence and responsible owners. The system connects reviewed obligations to scheduled work, submissions and corrective actions, helping the compliance team see what is complete and what still needs an accountable decision.
From intake to authorised completion, with evidence at each decision.
Register applicable obligations with accountable ownership.
Translate requirements into scheduled evidence and control tasks.
Review submissions and manage noncompliance actions.
Approve reporting and retain a traceable compliance record.
Permissions are configured and tested for the agreed responsibilities.
Interface scope, data mapping and testing are agreed for each engagement.
Review assigned evidence and approve permitted tasks from responsive views.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Organise supplied evidence against reviewer-approved requirements. Regulatory interpretation remains with qualified owners.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
An example operating scenario
An obligation is assigned to a responsible owner with an evidence deadline. A reviewer rejects an incomplete submission, the corrective action is completed and the approved reporting record links back to the interpreted obligation and its evidence.
Roles, approval authority, business rules, records and reporting are configured around your operating model. Scope definition connects the required business outcome to workflows, interfaces and acceptance criteria.
Operators, reviewers and authorised decision makers have defined responsibilities. Approval limits, exception handling and access permissions are agreed with your business owners and tested against the selected workflows.
Interface requirements cover your existing business systems, data ownership, mapping and authentication. Connection design and testing form part of the agreed implementation scope.
Start with a relevant business transaction, then review its approvals, an exception, role permissions and final records. Discuss the integrations, reporting and operating requirements that matter to your organisation.
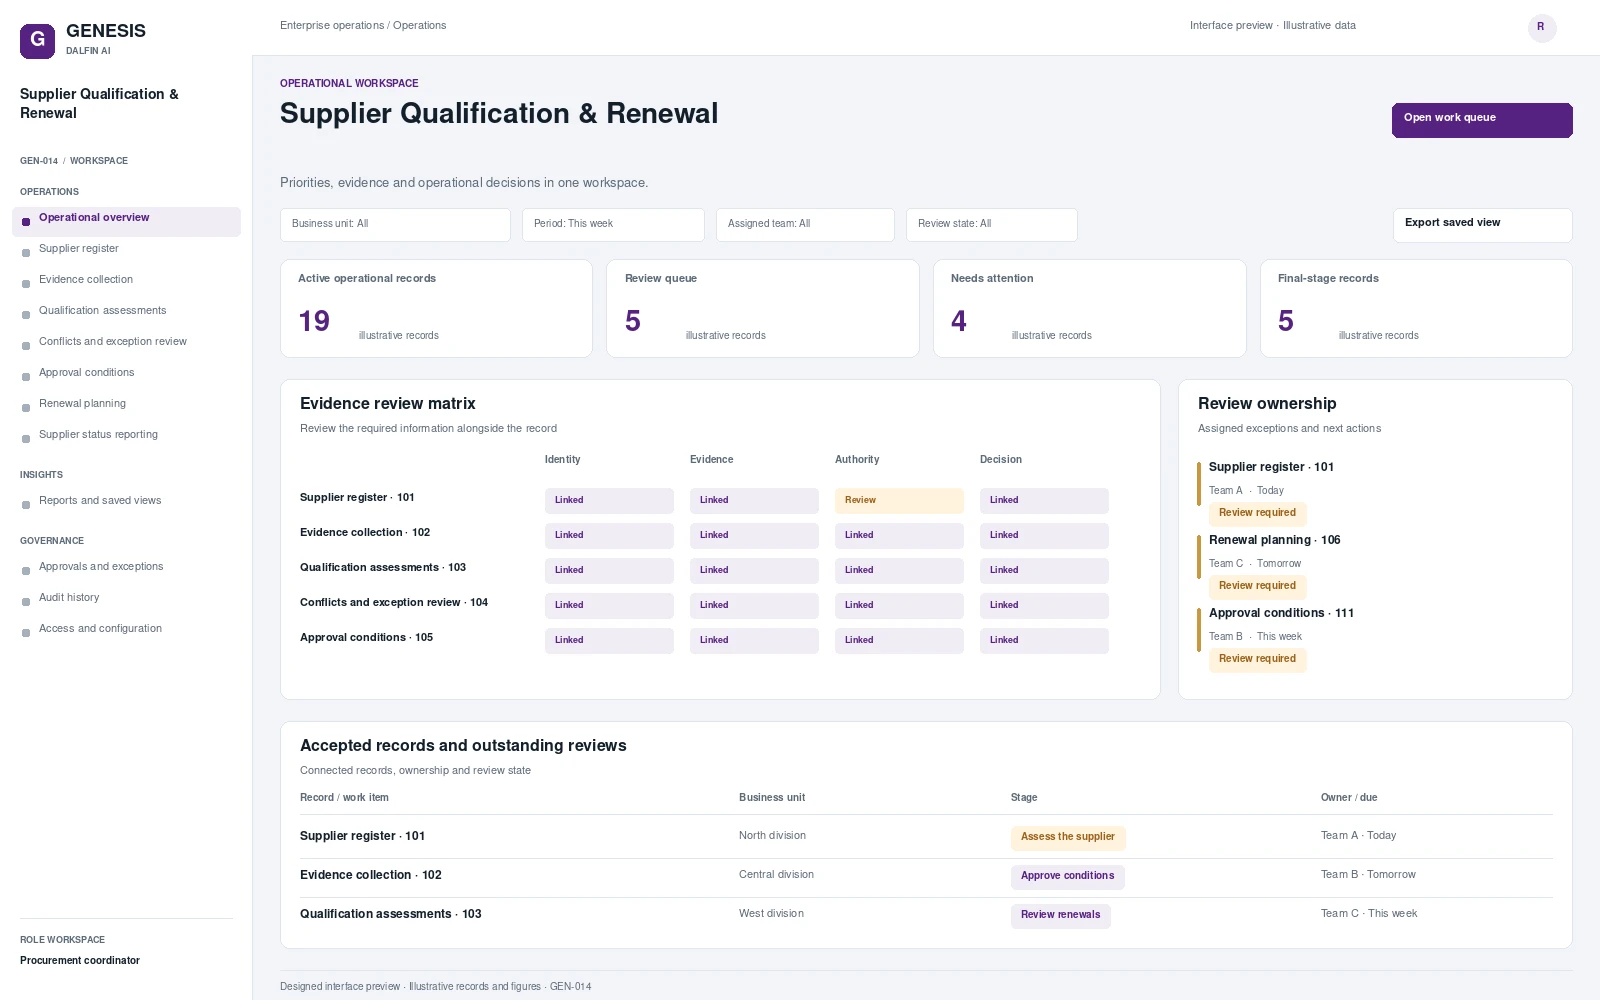 Interface preview
Coordinate supplier evidence, risk review, approval conditions and renewals in one accountable qualification process.
Explore system →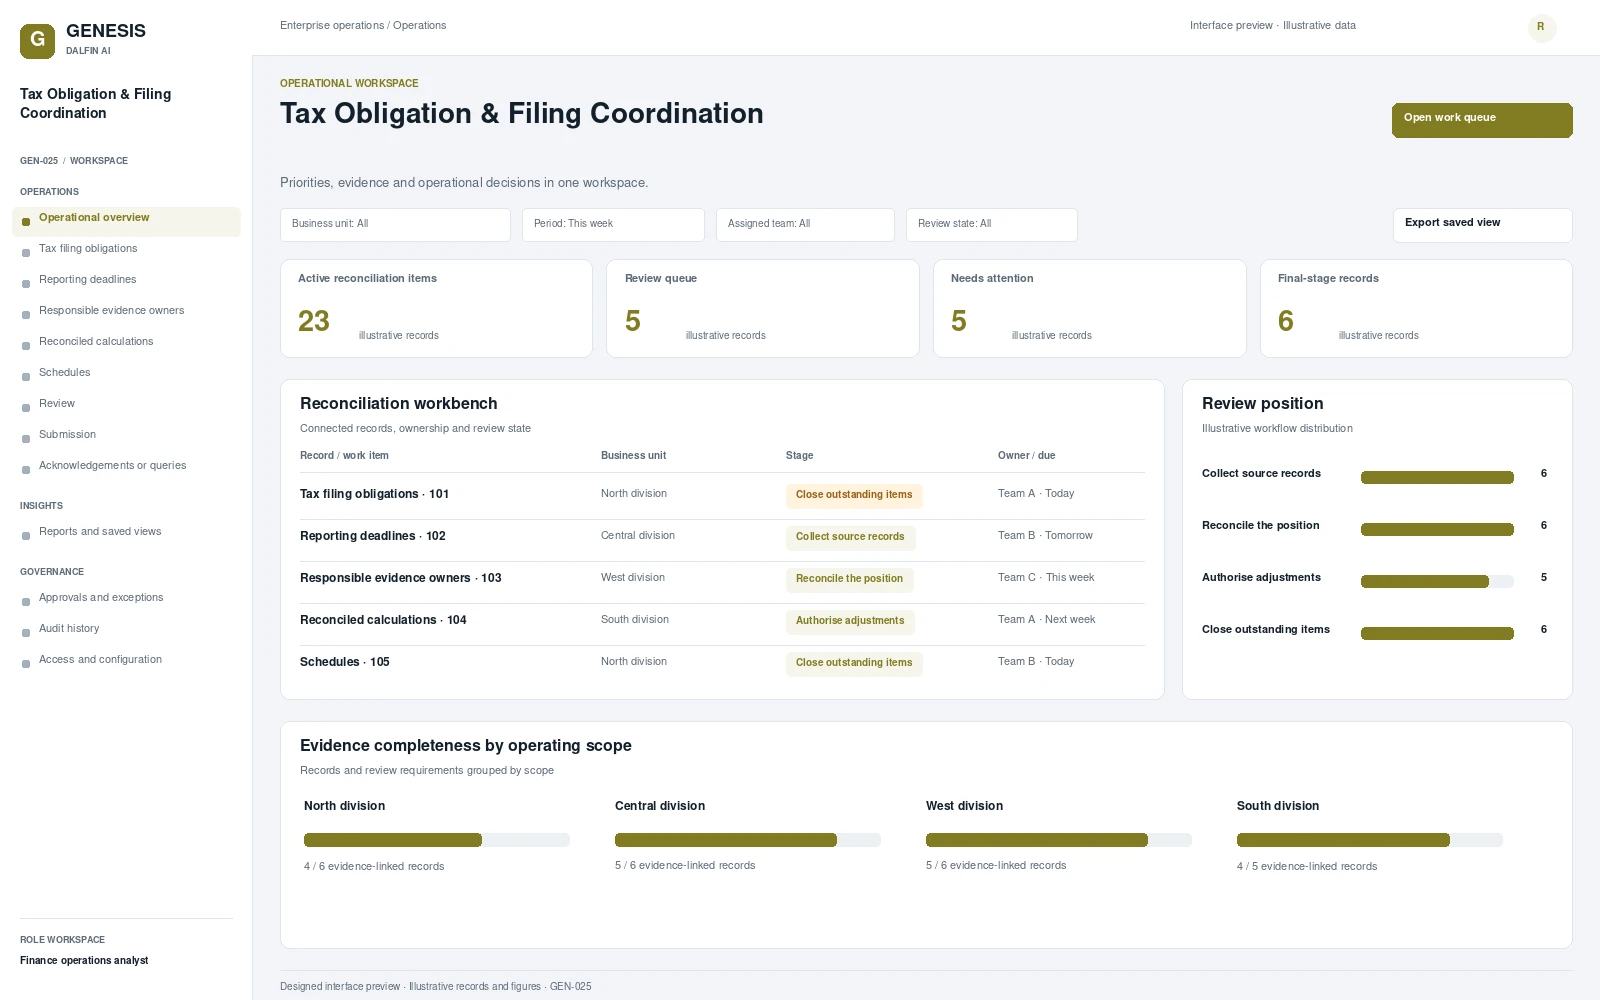 Interface preview
Tracks tax filing obligations, reporting deadlines and responsible evidence owners.
Explore system →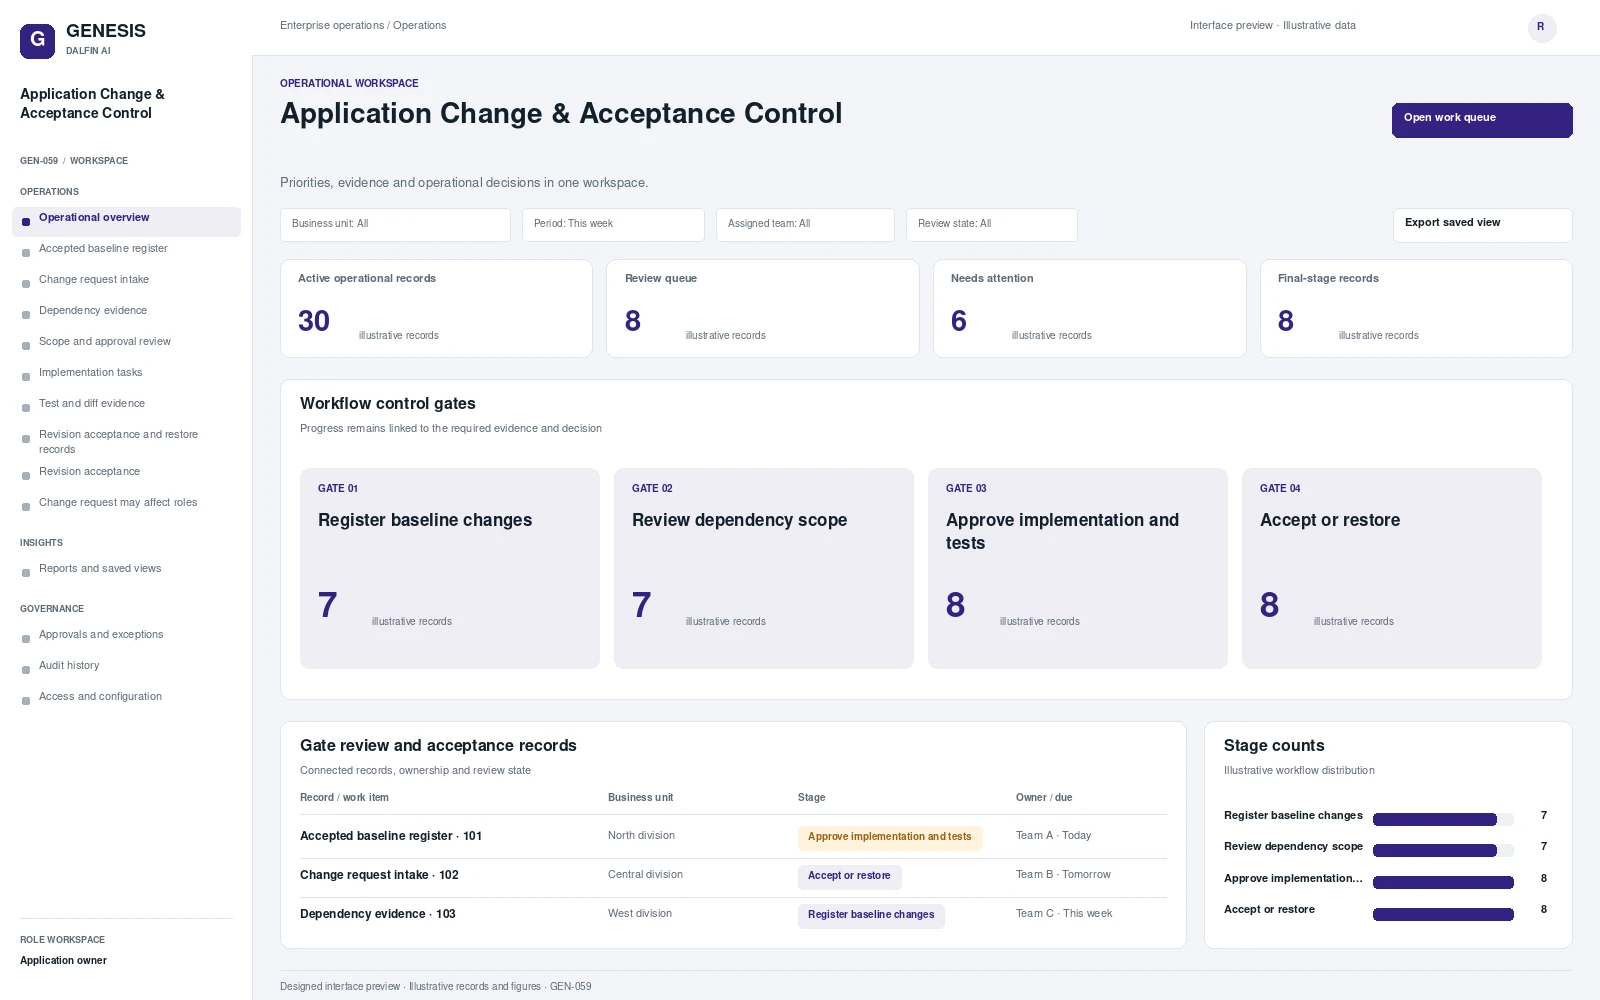 Interface preview
Govern change requests against an accepted application baseline, dependency evidence, implementation scope, tests and revision acceptance.
Explore system →