
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Central government / APPLICATION BLUEPRINT
Tracks time-sensitive evidence supporting identity document applications, identifies cases needing updated documents and sends approved requests.
11 workspace menus · 9 business workflows · 5 role profiles
Application blueprint only. This is a proposed design, not a deployed or production-tested system. Screens and sample figures are illustrative; workflows, business rules, approvals, permissions and integrations require confirmation before build.
Designed for programme officers and the responsible business owners
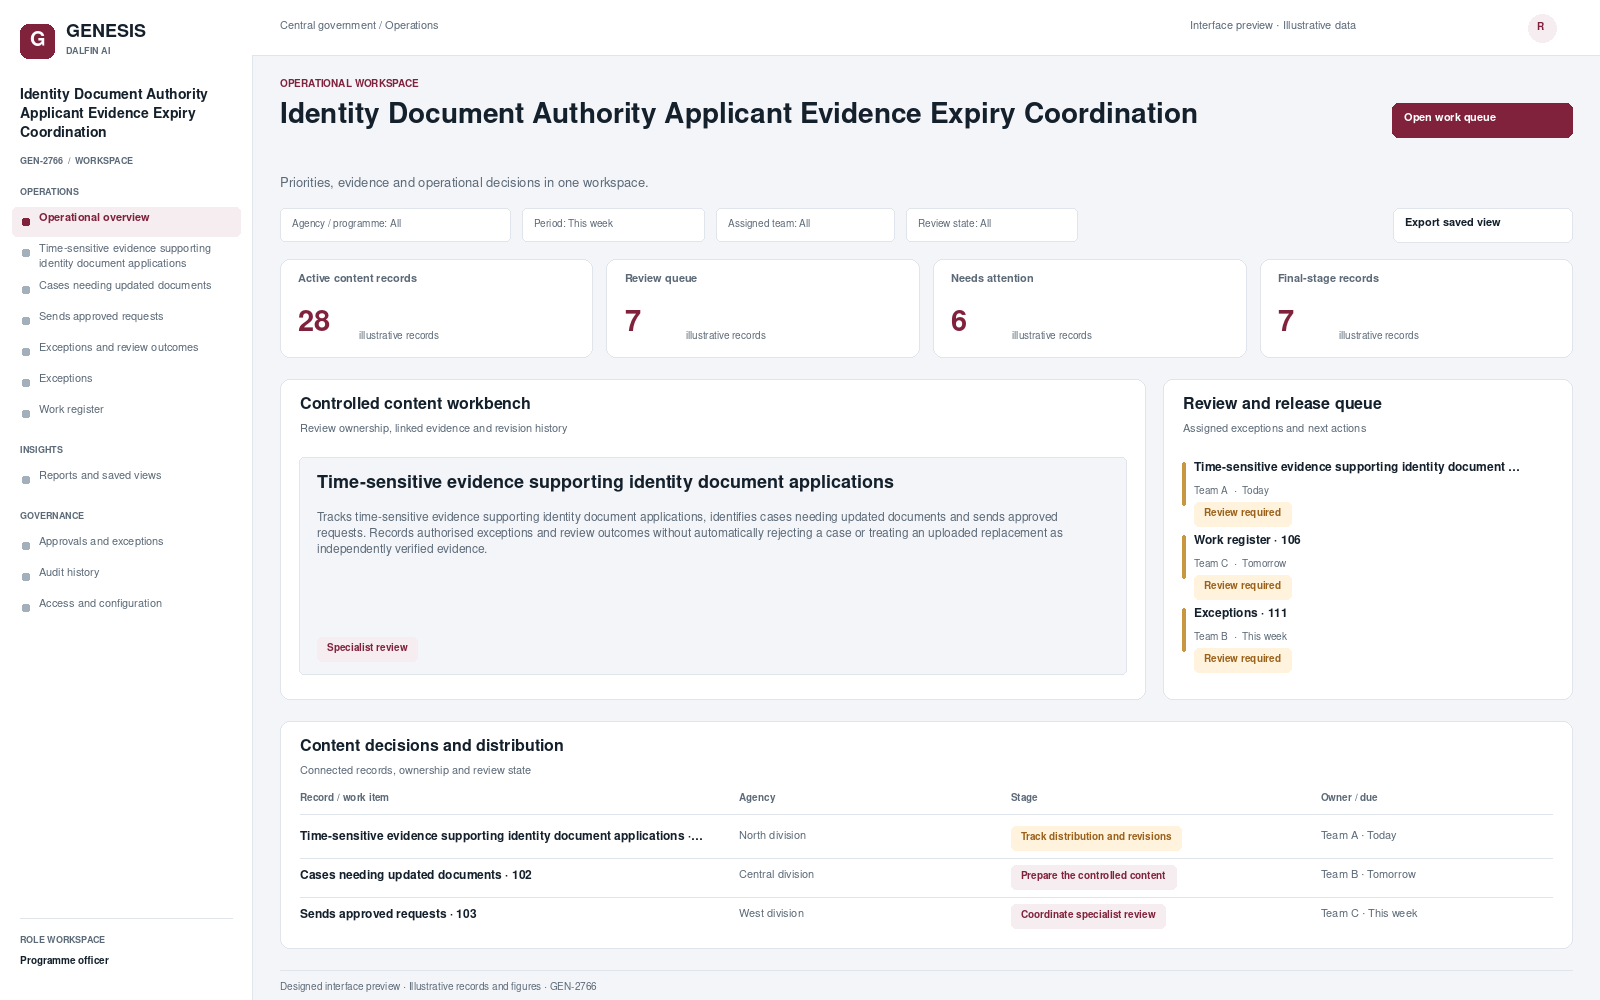
Illustrative workspace and record review. Select a concept screen to inspect it in full.
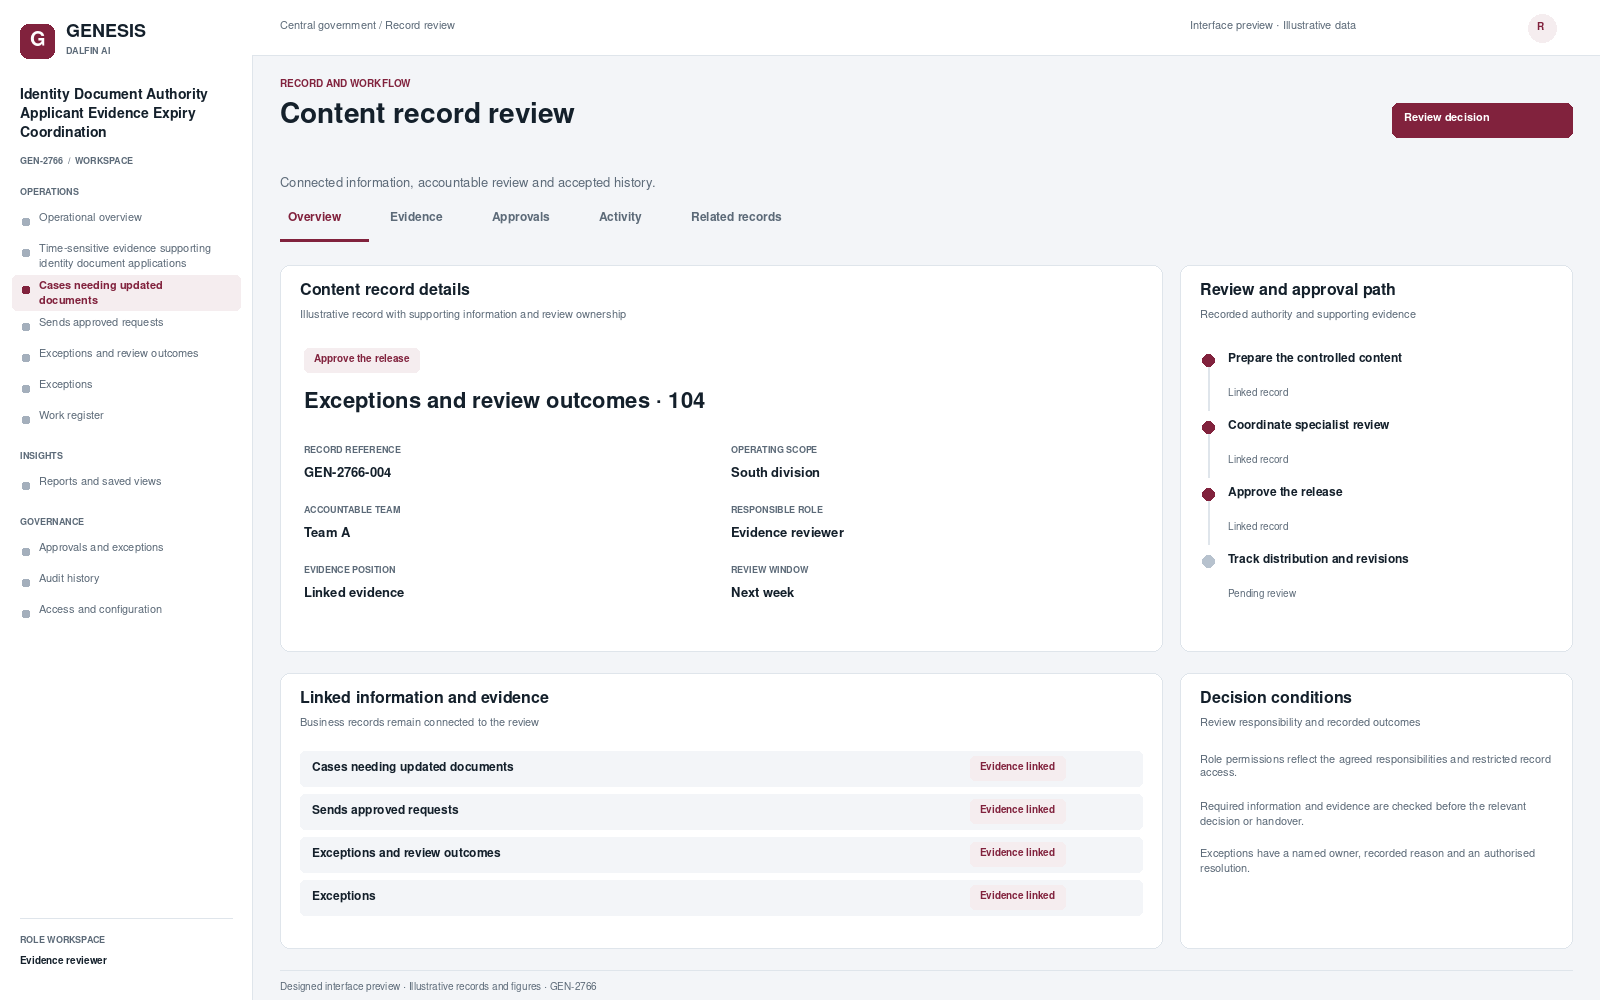
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Tracks time-sensitive evidence supporting identity document applications, identifies cases needing updated documents and sends approved requests. Records authorised exceptions and review outcomes without automatically rejecting a case or treating an uploaded replacement as independently verified evidence.
From intake to authorised completion, with evidence at each decision.
Establish the scope of time-sensitive evidence supporting identity document applications, capture the required records and assign the accountable team.
Coordinate cases needing updated documents, sends approved requests, with linked evidence and visible outstanding actions.
Review the relevant conditions and exceptions. Record the authorised outcome and its supporting evidence.
Confirm the resulting records and handovers. Track remaining obligations, later changes and follow-up actions.
Select a workflow to review the steps, responsibilities, approval and exception handling.
Coordinate time-sensitive evidence supporting identity document applications within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Time-sensitive evidence supporting identity document applications requires a new record, an agreed review or a controlled change.
Responsible role
Evidence reviewer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate cases needing updated documents within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Cases needing updated documents requires a new record, an agreed review or a controlled change.
Responsible role
Programme officer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Content conflicts, missing review or a changed recipient permission prevents release.
Outcome
An accepted content version with distribution and revision history.
Coordinate sends approved requests within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Sends approved requests requires a new record, an agreed review or a controlled change.
Responsible role
Programme officer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
The case exceeds delegation, contains a conflict or has disputed evidence.
Outcome
An authorised decision or escalation with accountable resolution actions.
Coordinate authorised exceptions and review outcomes within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Authorised exceptions and review outcomes requires a new record, an agreed review or a controlled change.
Responsible role
Evidence reviewer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate operating requirement within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Operating requirement requires a new record, an agreed review or a controlled change.
Responsible role
Programme officer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
An assumption changes, prerequisites are missing or stakeholders cannot accept the proposed commitment.
Outcome
An approved operating plan and owned actions for its accepted conditions.
Coordinate operating exceptions within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Operating exceptions requires a new record, an agreed review or a controlled change.
Responsible role
Programme officer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
The case exceeds delegation, contains a conflict or has disputed evidence.
Outcome
An authorised decision or escalation with accountable resolution actions.
Coordinate completion and follow-up within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Completion and follow-up requires a new record, an agreed review or a controlled change.
Responsible role
Evidence reviewer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate controlled operating changes within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Controlled operating changes requires a new record, an agreed review or a controlled change.
Responsible role
Evidence reviewer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Evidence is incomplete, disputed, expired or outside the reviewer’s authority.
Outcome
A review finding, its accepted evidence and any accountable corrective actions.
Coordinate scoped operational reports within Identity Document Authority Applicant Evidence Expiry Coordination.
Trigger
Scoped operational reports requires a new record, an agreed review or a controlled change.
Responsible role
Programme officer
Approval
Delegated decision maker records the decision when the action changes an accepted commitment or requires delegated authority.
Exception handling
Required information or responsibility is missing, or an operating condition changes.
Outcome
A completed operating record with its linked evidence and remaining obligations.
Interface scope, data mapping and testing are agreed for each engagement.
Authorised users can review time-sensitive evidence supporting identity document applications, supporting records and assigned actions through mobile and tablet access. The relevant tasks and permissions are agreed for the deployment.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Core workflows and approval rules are defined with your business owners. Operational AI can be assessed separately against a specific business outcome and review requirements.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
AN EXAMPLE OPERATING SCENARIO
Start with time-sensitive evidence supporting identity document applications and follow the record through coordinate specialist review. Introduce a missing item or operating exception, record the authorised resolution and inspect the final handover, evidence and history.
Review a representative content record, its workflow stages, accountable roles, an exception and the resulting operational report. Bring the business process and existing system requirements that matter to your organisation.
The operating scope covers your records, role permissions, review authority, business rules and integration boundaries. These requirements are agreed with the responsible business owners.
Connection design defines interfaces, data ownership, mapping, authentication and exception handling. The agreed implementation includes validation against the selected systems and workflows.
The agreed engineering approach covers review of change impact, bounded implementation, validation and accepted revisions. Discuss the relevant Genesis Context Memory and support requirements during solution scoping.
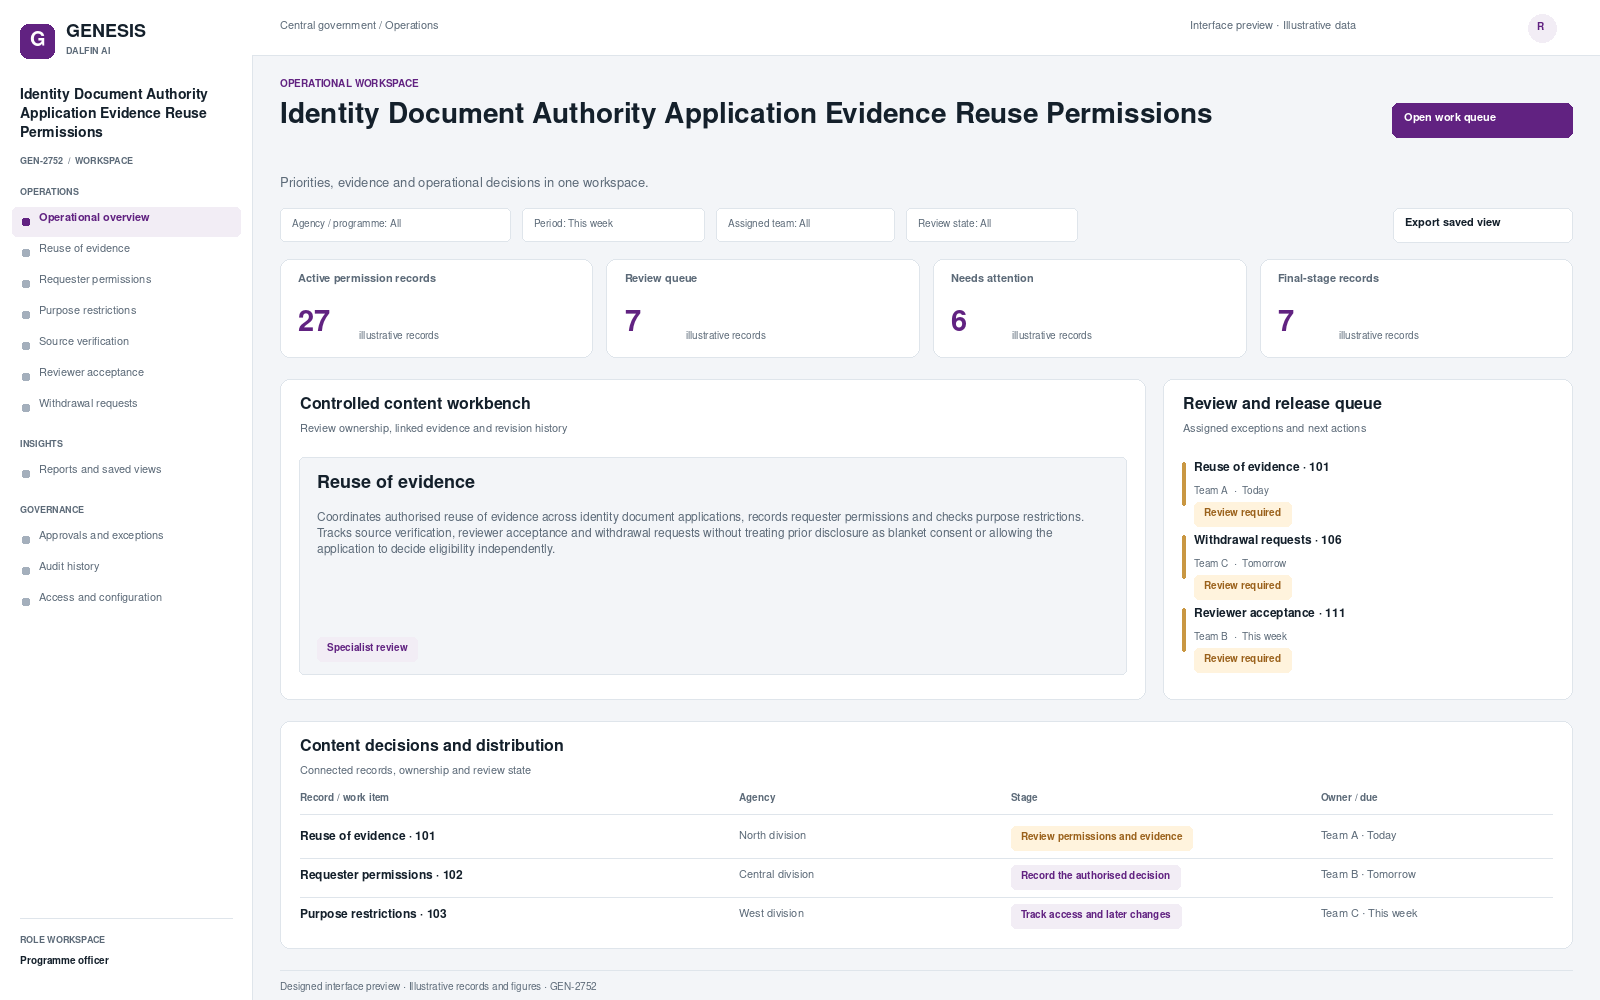 Interface preview
Coordinates authorised reuse of evidence across identity document applications, records requester permissions and checks purpose restrictions.
View blueprint →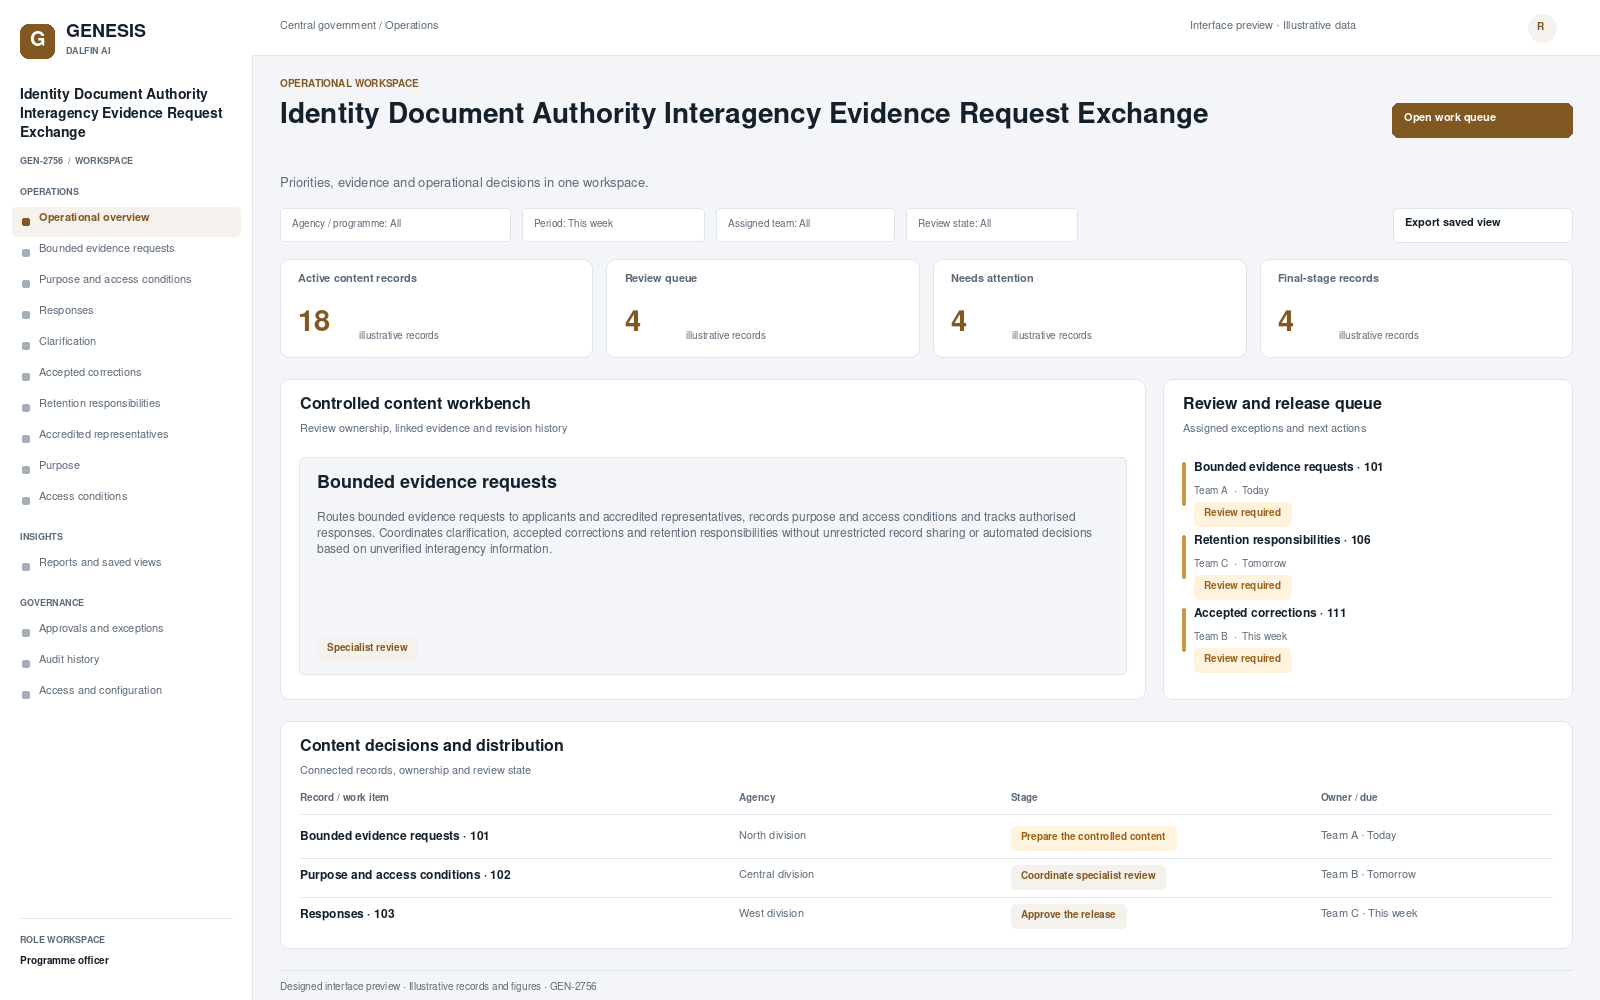 Interface preview
Routes bounded evidence requests to applicants and accredited representatives, records purpose and access conditions and tracks authorised responses.
View blueprint →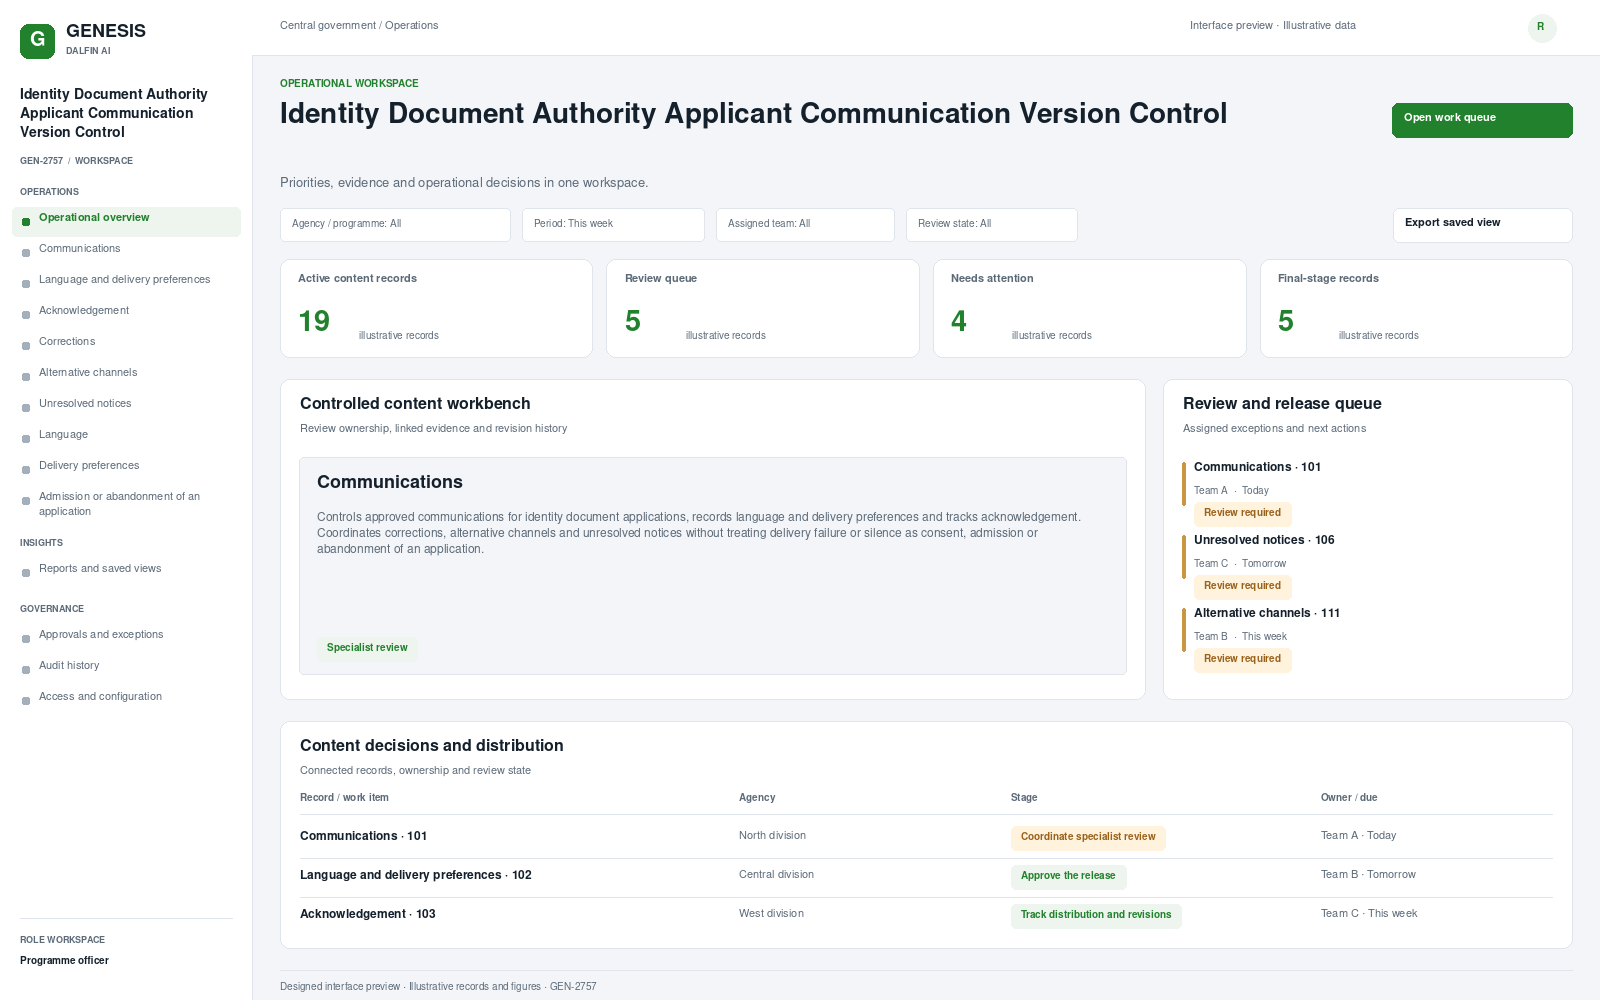 Interface preview
Controls approved communications for identity document applications, records language and delivery preferences and tracks acknowledgement.
View blueprint →