
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Pharmaceuticals & biotechnology
Coordinate suspected adverse-event intake, missing-information follow-up, qualified medical review and approved reporting records.
12 workspace menus · 5 role profiles · Connected records
Designed for drug safety operations directors
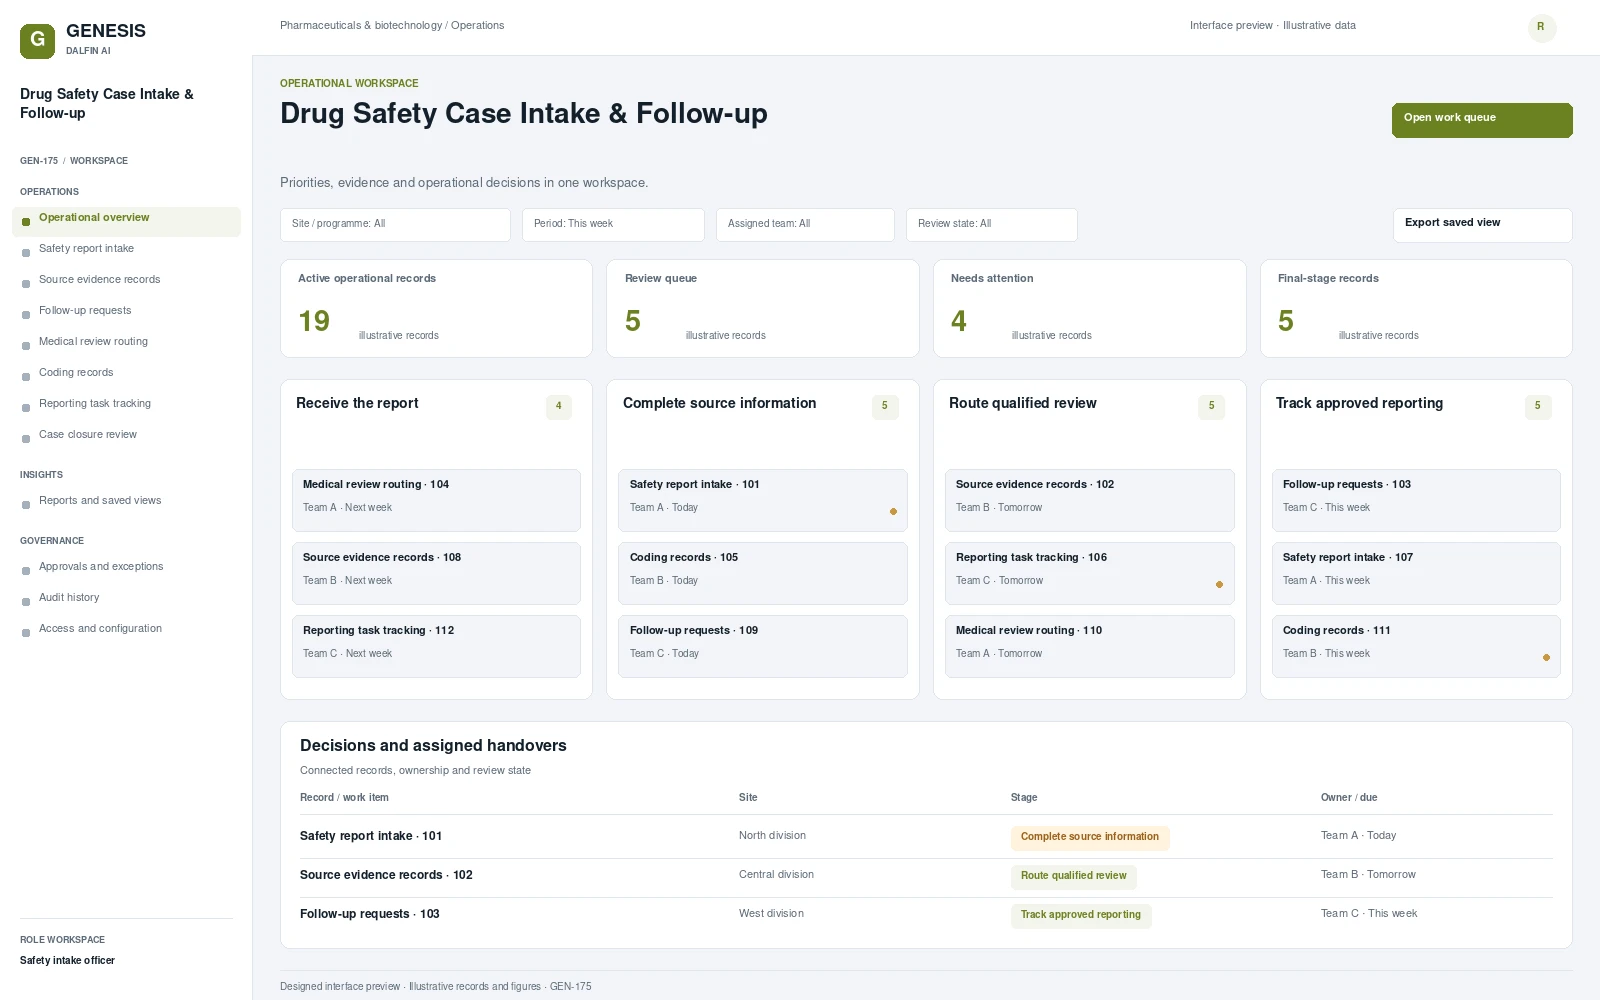
Operational workspace and record review. Select a screen to inspect it in full.
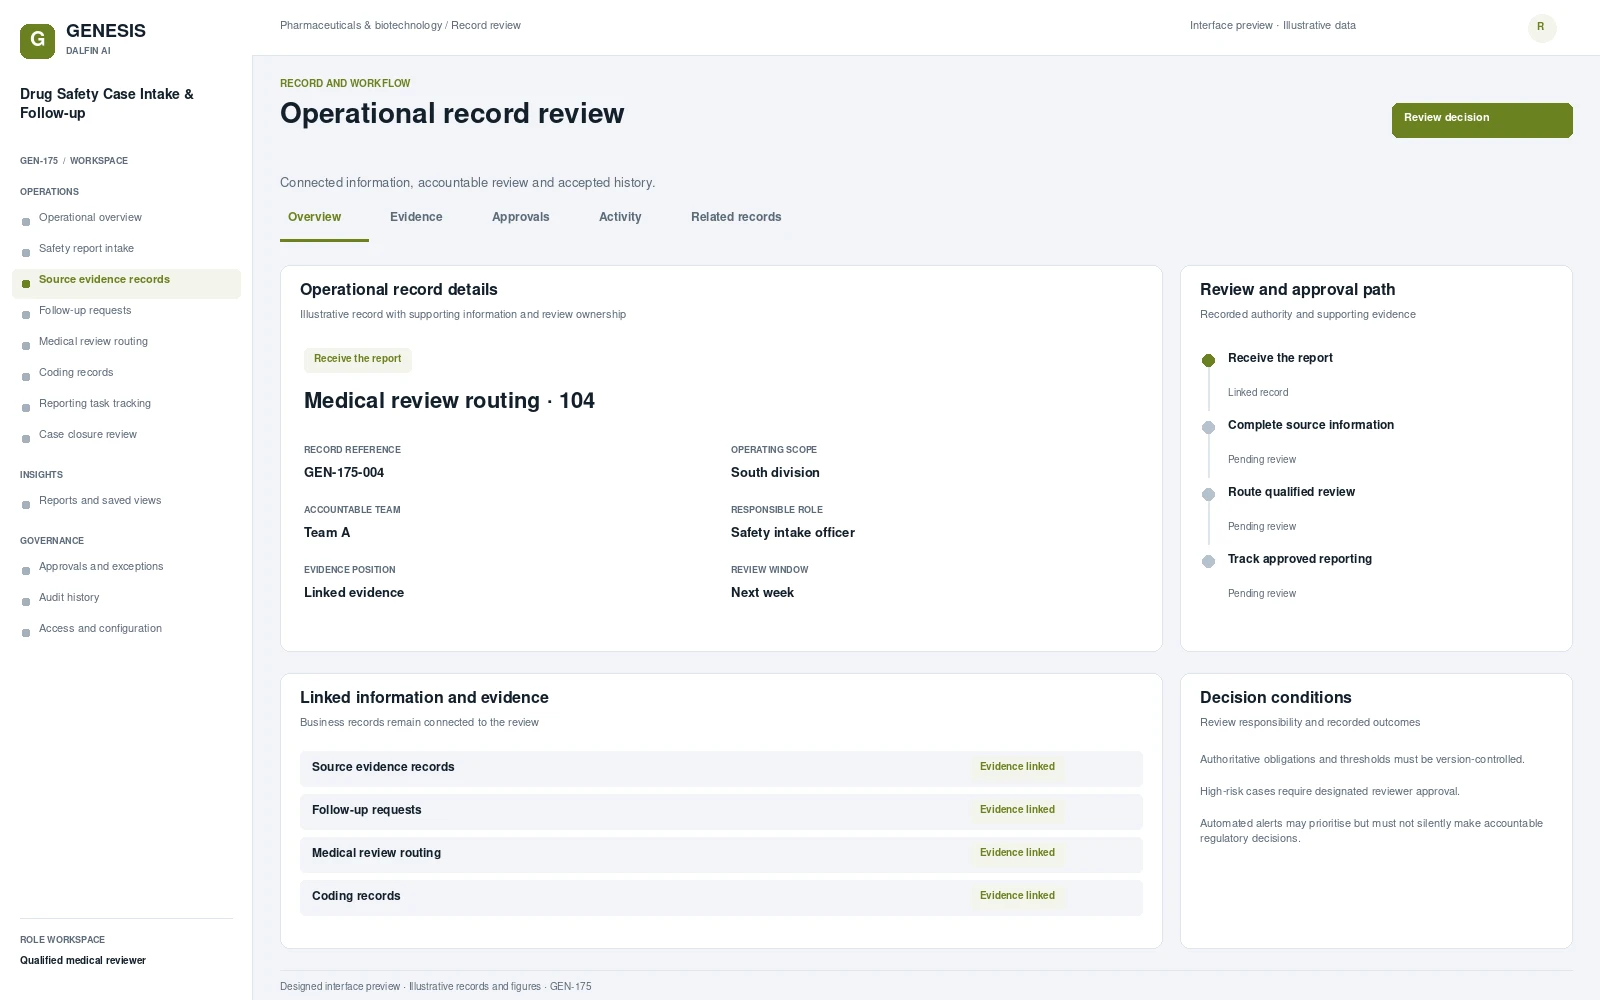
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Coordinate suspected adverse-event intake, missing-information follow-up, qualified medical review and approved reporting records. A safety case can lose important context as source reports, follow-up requests and review decisions move between teams. The system connects intake to case closure with accountable review steps, preserving the source evidence and the approved reporting position for each case.
From intake to authorised completion, with evidence at each decision.
Receive suspected adverse event report.
Collect missing source information.
Route medical review and coding.
Track approved reporting and case closure.
Permissions are configured and tested for the agreed responsibilities.
Interface scope, data mapping and testing are agreed for each engagement.
Responsive intake or reviewer access can be scoped under approved privacy and validation requirements.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Prepare a draft evidence summary for medical reviewer confirmation. Causality, seriousness and reportability remain qualified-review decisions.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
An example operating scenario
A suspected adverse-event report lacks source information. The coordinator issues a follow-up request, the qualified reviewer records the medical assessment and approved coding, and the reporting officer tracks the authorised reporting tasks before closure.
Roles, approval authority, business rules, records and reporting are configured around your operating model. Scope definition connects the required business outcome to workflows, interfaces and acceptance criteria.
Operators, reviewers and authorised decision makers have defined responsibilities. Approval limits, exception handling and access permissions are agreed with your business owners and tested against the selected workflows.
Interface requirements cover your existing business systems, data ownership, mapping and authentication. Connection design and testing form part of the agreed implementation scope.
Start with a relevant business transaction, then review its approvals, an exception, role permissions and final records. Discuss the integrations, reporting and operating requirements that matter to your organisation.
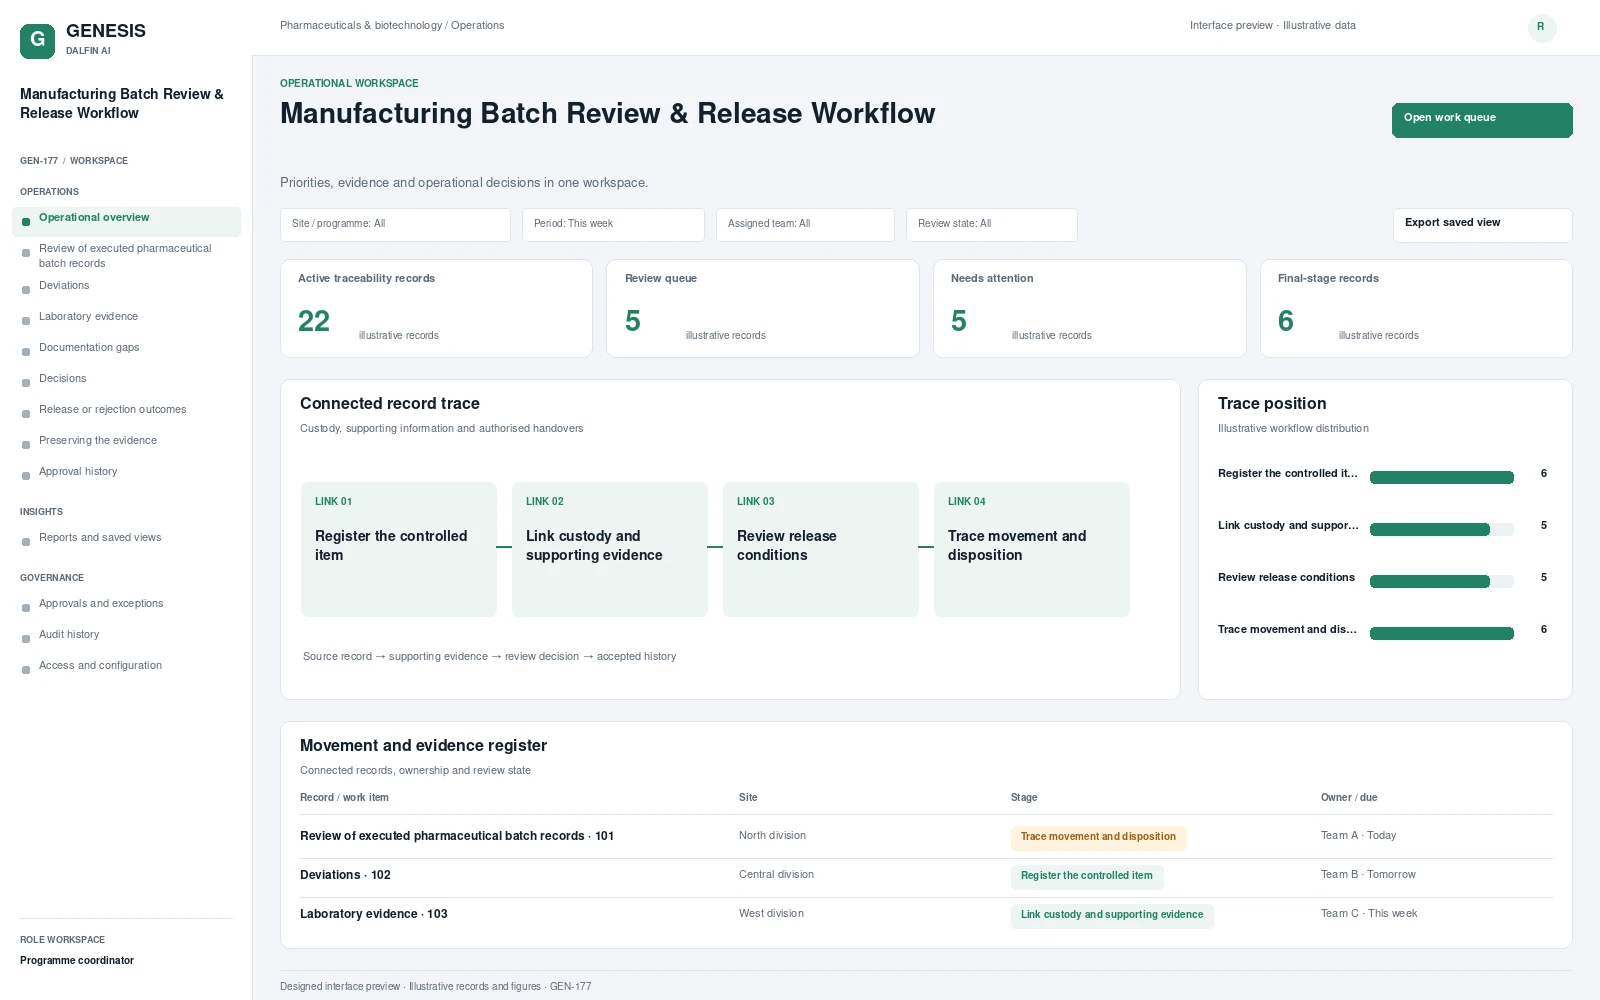 Interface preview
Coordinates review of executed pharmaceutical batch records, deviations and laboratory evidence.
Explore system →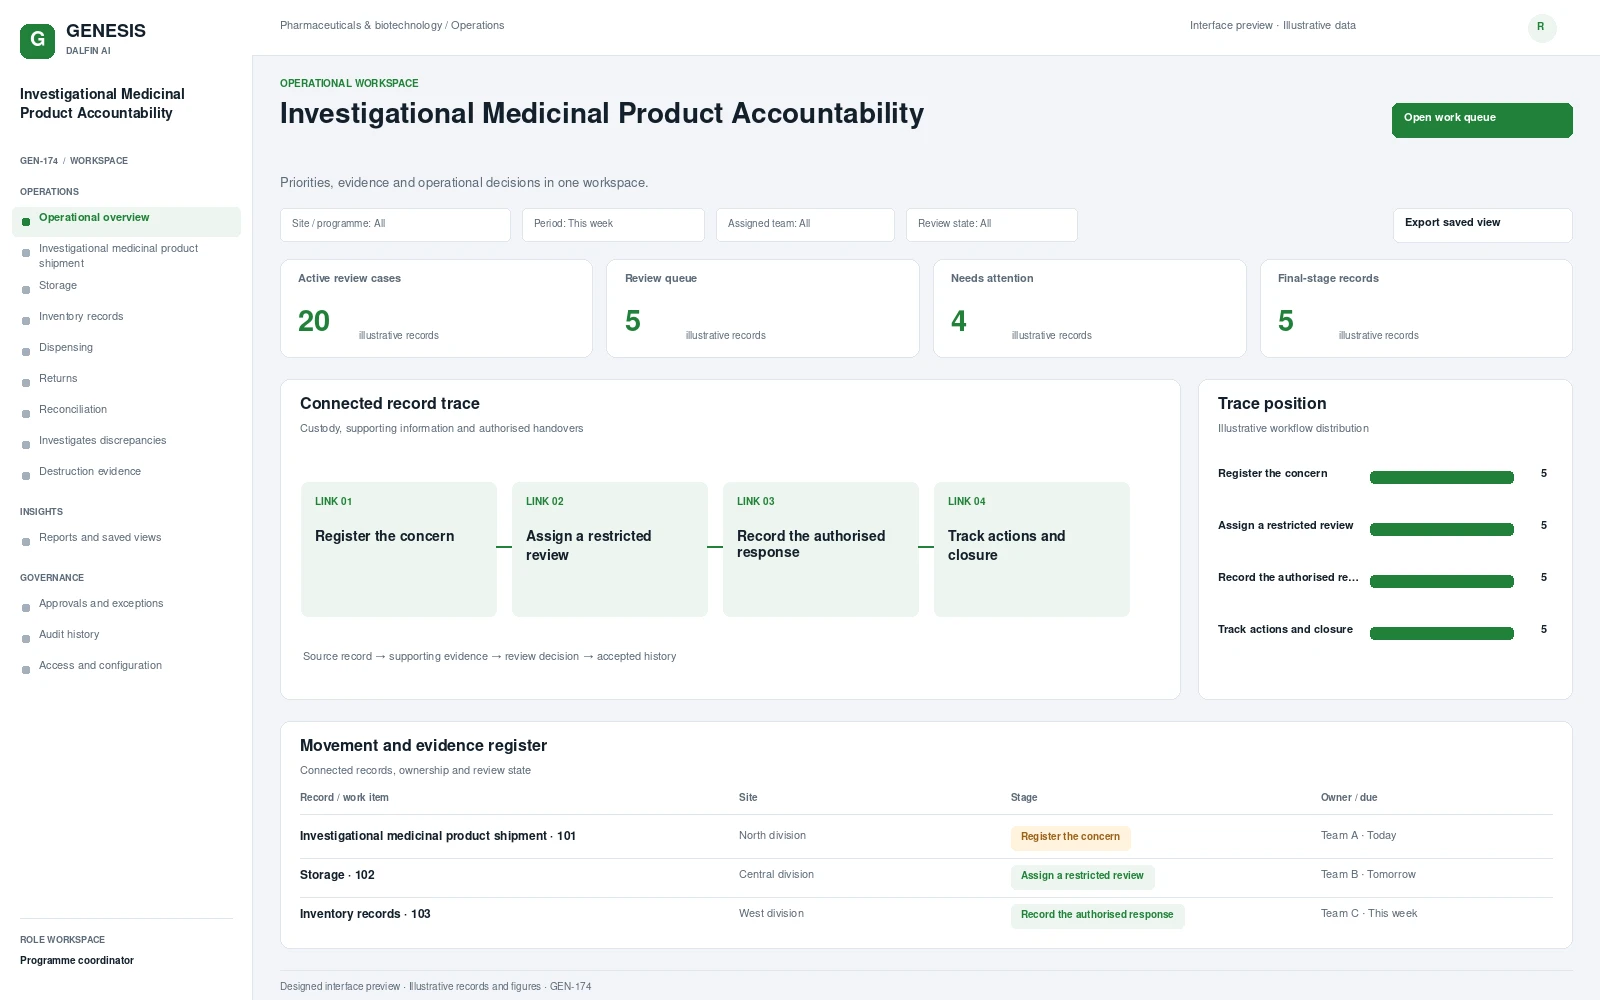 Interface preview
Maintains investigational medicinal product shipment, storage and inventory records.
Explore system → Interface preview
Assists regulatory drafting using bounded, approved source material.
Explore system →