
Operational views
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Enterprise operations
Coordinate validated incident reports, evidence preservation, authorised response actions, restoration review and corrective follow-up.
12 workspace menus · 5 role profiles · Connected records
Designed for security operations leads and incident commanders
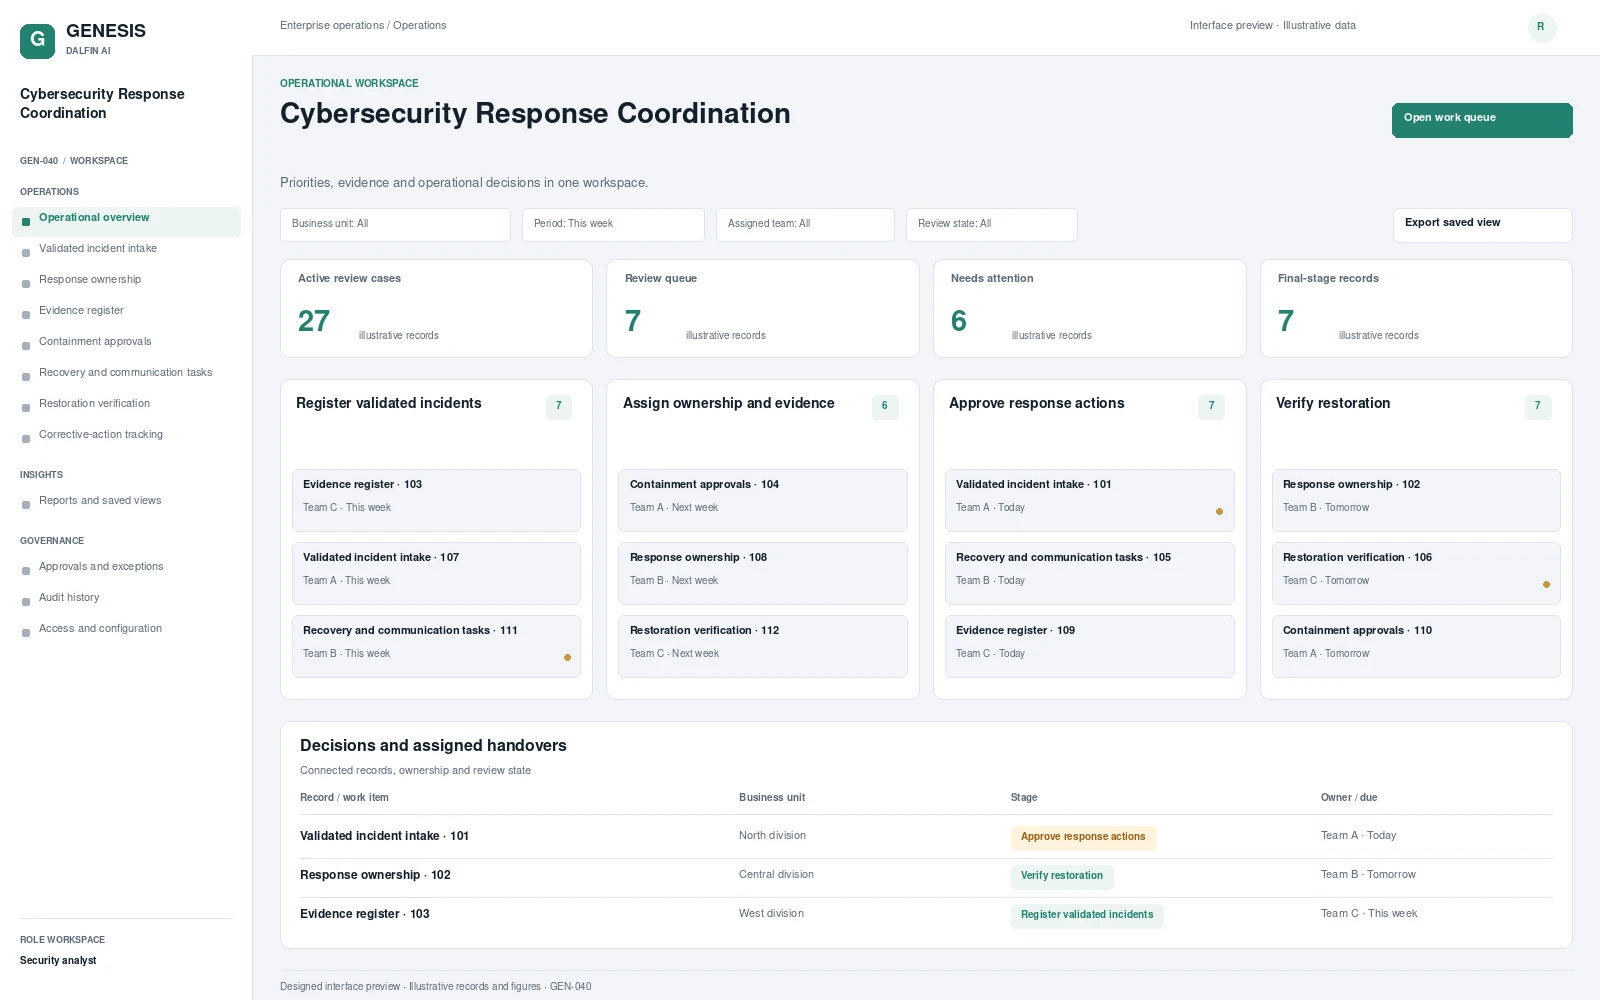
Operational workspace and record review. Select a screen to inspect it in full.
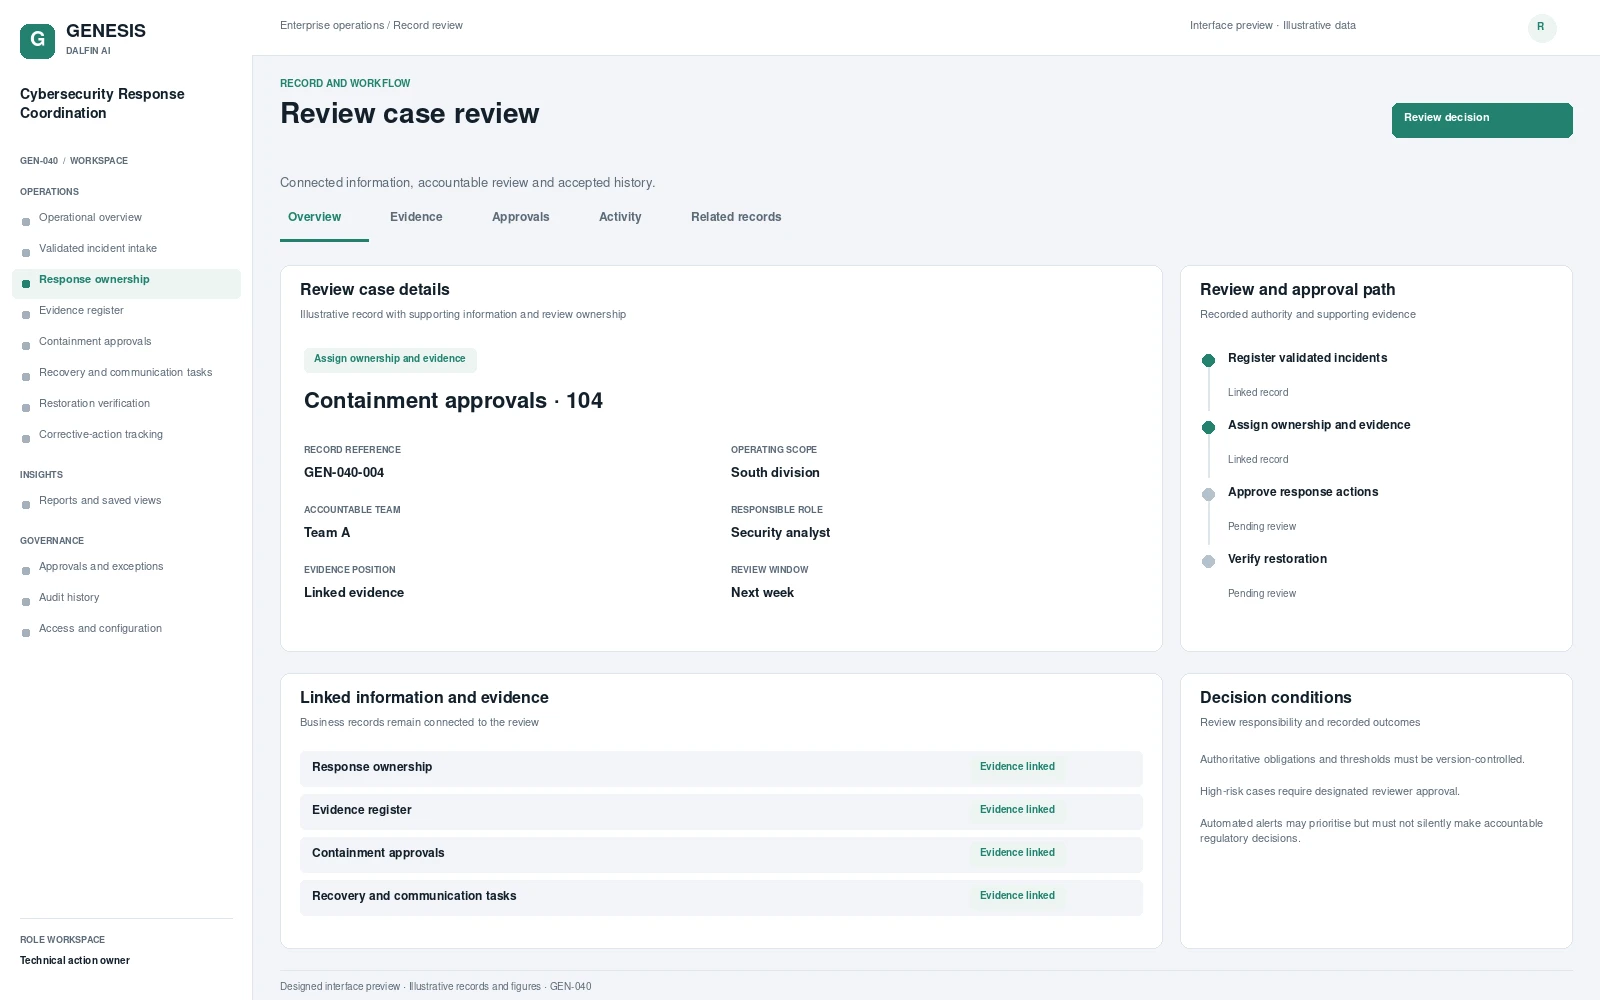
Review work, evidence, exceptions and authorised decisions within a defined operating scope.
Coordinate validated incident reports, evidence preservation, authorised response actions, restoration review and corrective follow-up. During an incident, ownership and approval records can become fragmented across technical tools and communication channels. This administrative scope connects evidence and authorised actions to the response record, preserving who approved containment, recovery and communication before corrective tasks are closed.
From intake to authorised completion, with evidence at each decision.
Receive a validated security alert or incident report.
Assign response ownership and preserve relevant evidence.
Approve containment, recovery and communication actions.
Verify restoration and close corrective follow-up tasks.
Permissions are configured and tested for the agreed responsibilities.
Interface scope, data mapping and testing are agreed for each engagement.
Review assigned administrative actions on approved devices. Automated remediation requires separately authorised controls.
Access approved workflows through the Dalfin mobile app. Device tasks and permissions are confirmed for the deployment.
Draft an incident timeline from approved records for commander review.
AI extensions are scoped around the required data, business outcome and review controls.
Connect requirements, roles, records, workflows and interfaces through the agreed Genesis engineering process.
Review dependency impact and validation requirements. Context Memory supports governed changes and accepted application revisions.
Agree customer cloud or on-premises requirements, device access, implementation acceptance and ongoing engineering support.
An example operating scenario
A validated incident is assigned to a response owner. A containment request requires authorised approval, recovery evidence is reviewed and restoration is verified. The workflow retains the response history and follows outstanding corrective actions to closure.
Roles, approval authority, business rules, records and reporting are configured around your operating model. Scope definition connects the required business outcome to workflows, interfaces and acceptance criteria.
Operators, reviewers and authorised decision makers have defined responsibilities. Approval limits, exception handling and access permissions are agreed with your business owners and tested against the selected workflows.
Interface requirements cover your existing business systems, data ownership, mapping and authentication. Connection design and testing form part of the agreed implementation scope.
Start with a relevant business transaction, then review its approvals, an exception, role permissions and final records. Discuss the integrations, reporting and operating requirements that matter to your organisation.
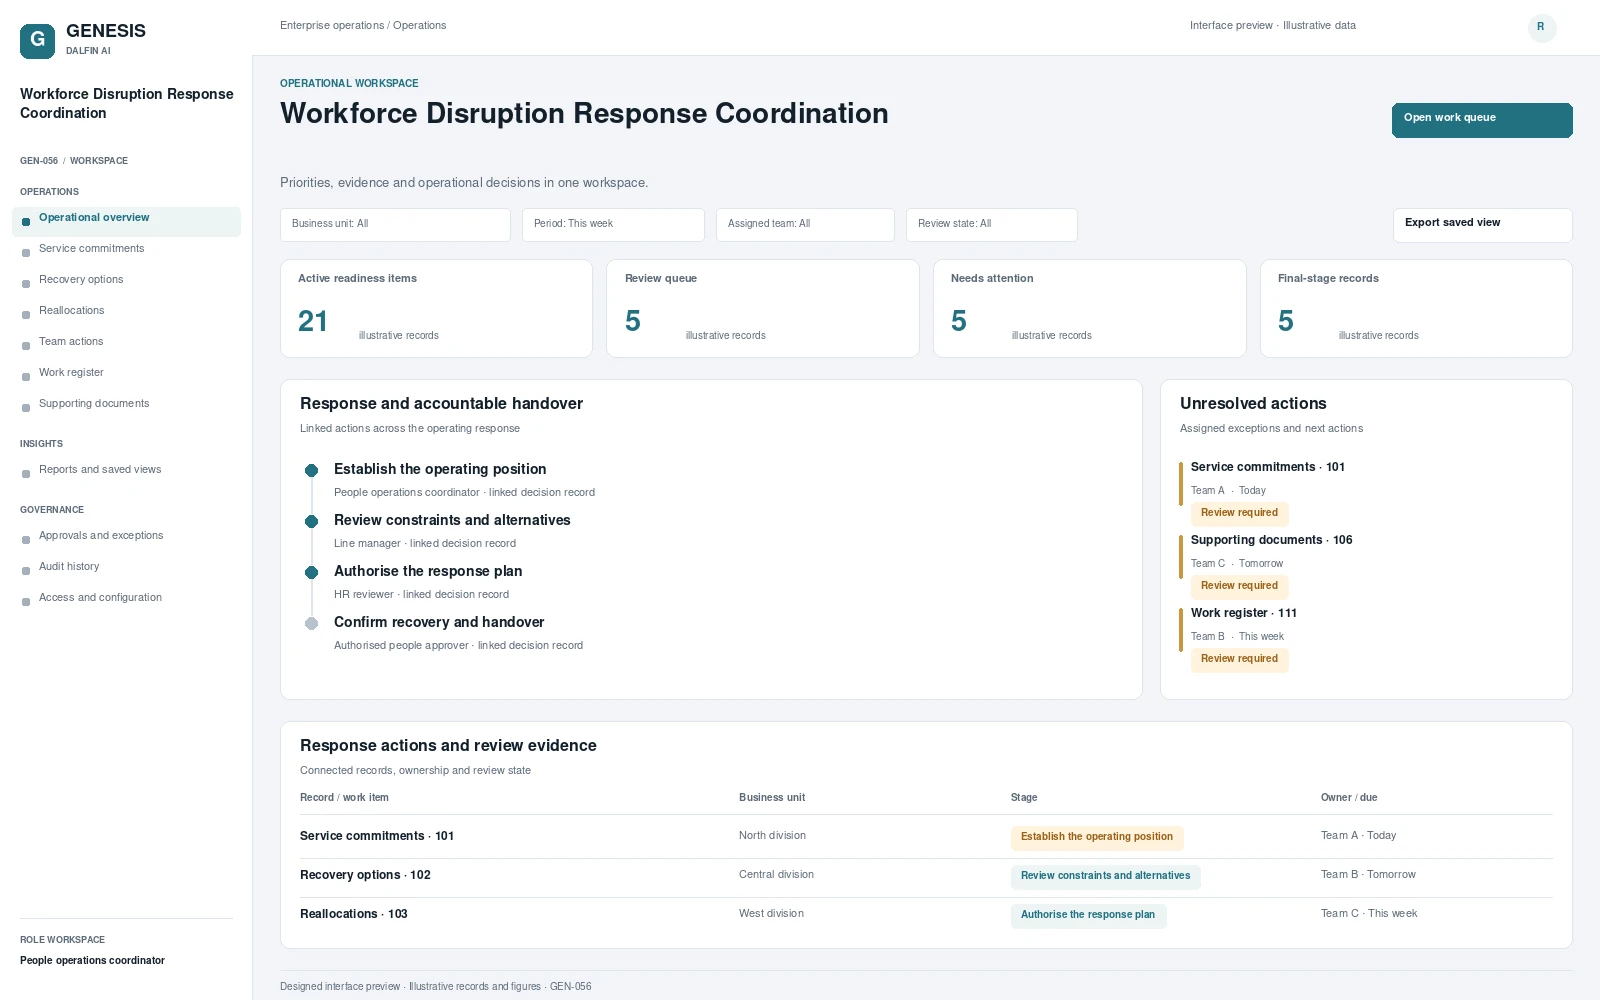 Interface preview
Coordinates the operational response to workforce disruptions affecting staffing and service commitments.
Explore system →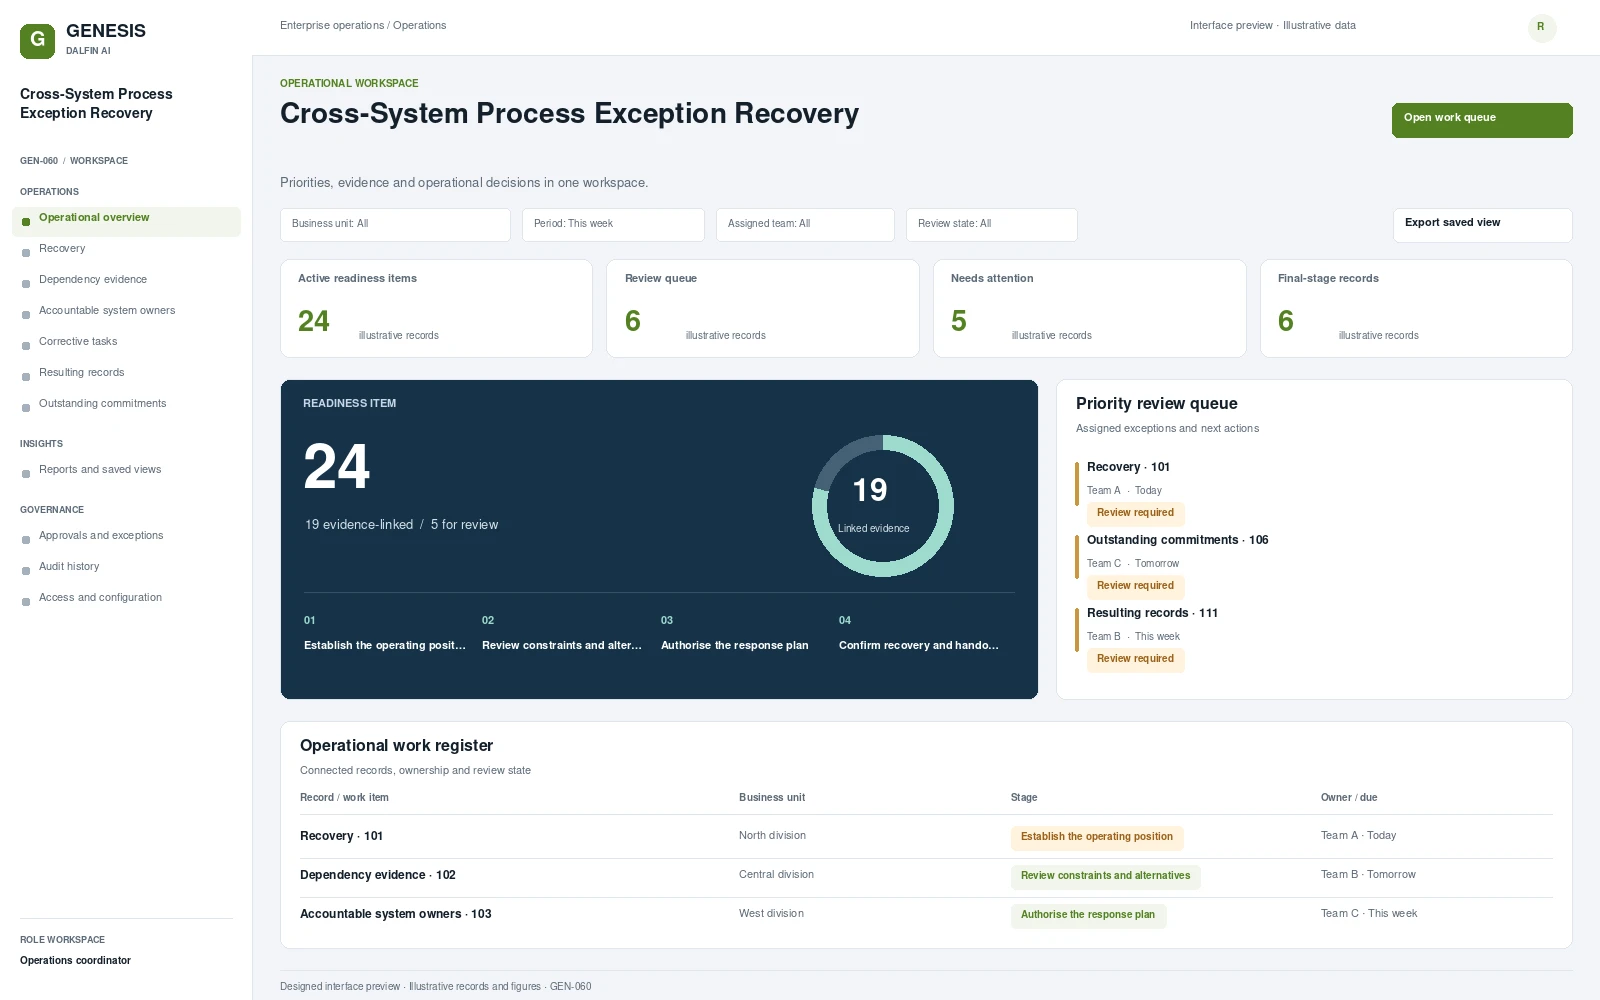 Interface preview
Coordinates recovery when a business transaction fails across connected systems.
Explore system →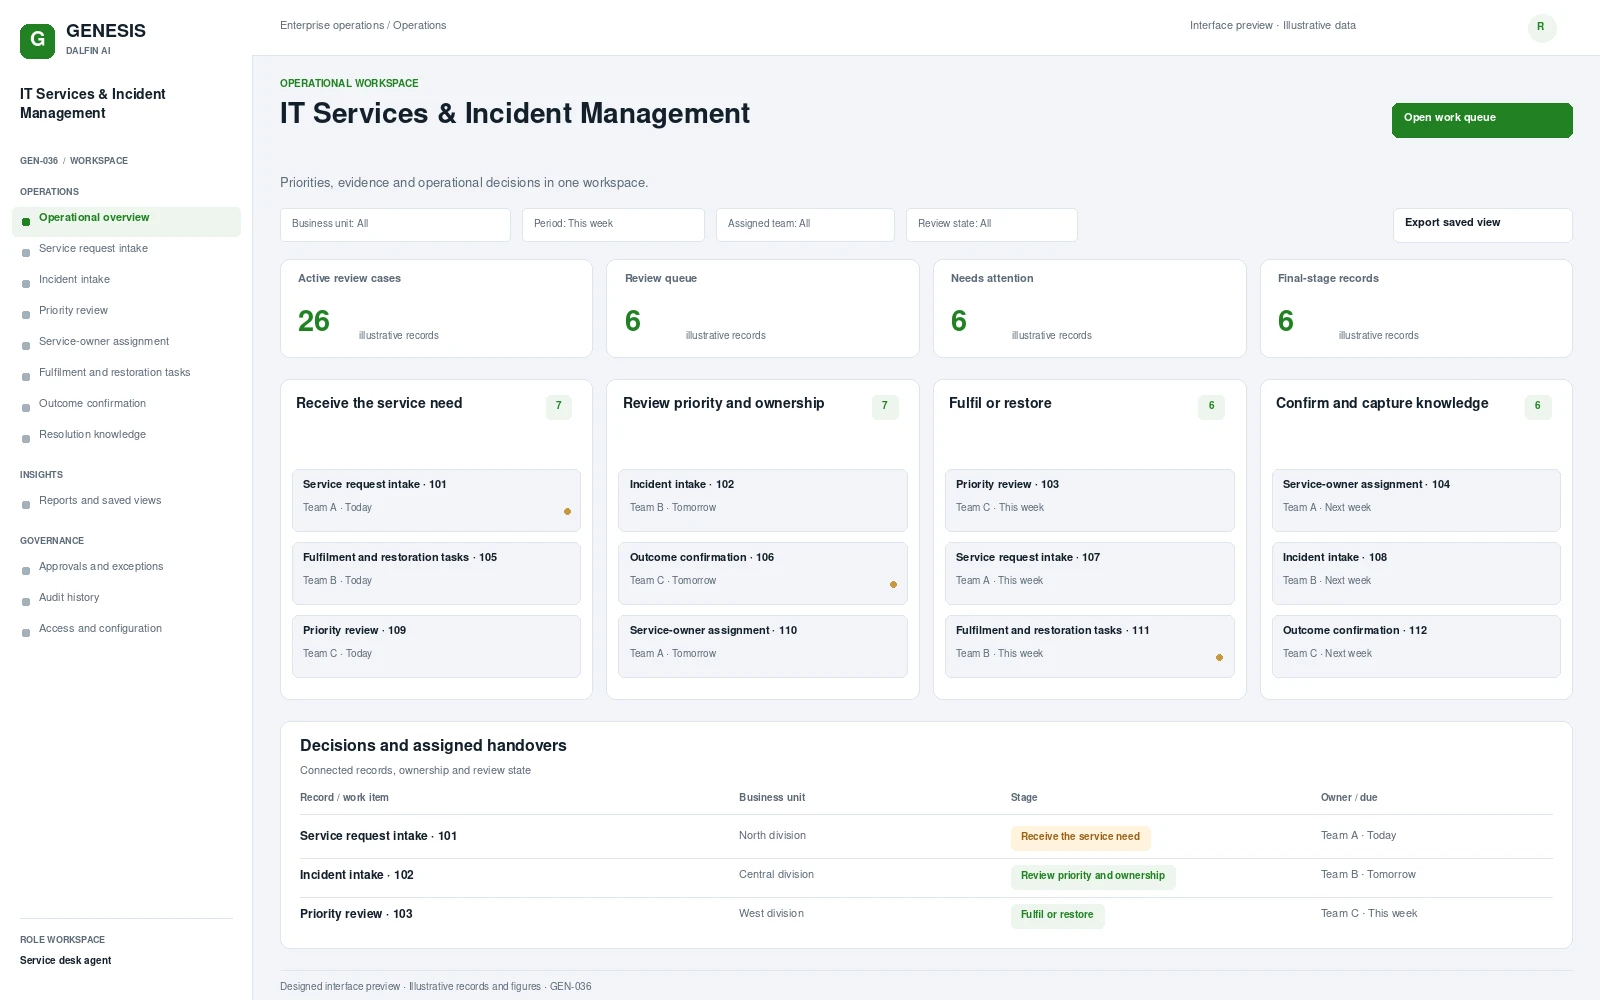 Interface preview
Coordinate service intake, priority review, accountable ownership, approved fulfilment, restoration and reusable resolution knowledge.
Explore system →